SecurityZines.com
Understanding Canary Tokens
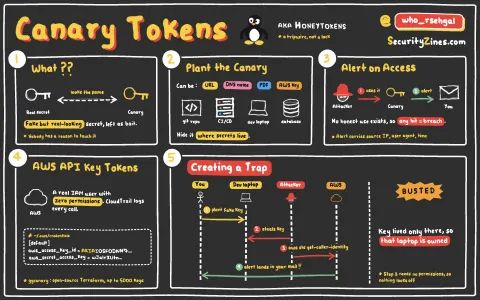
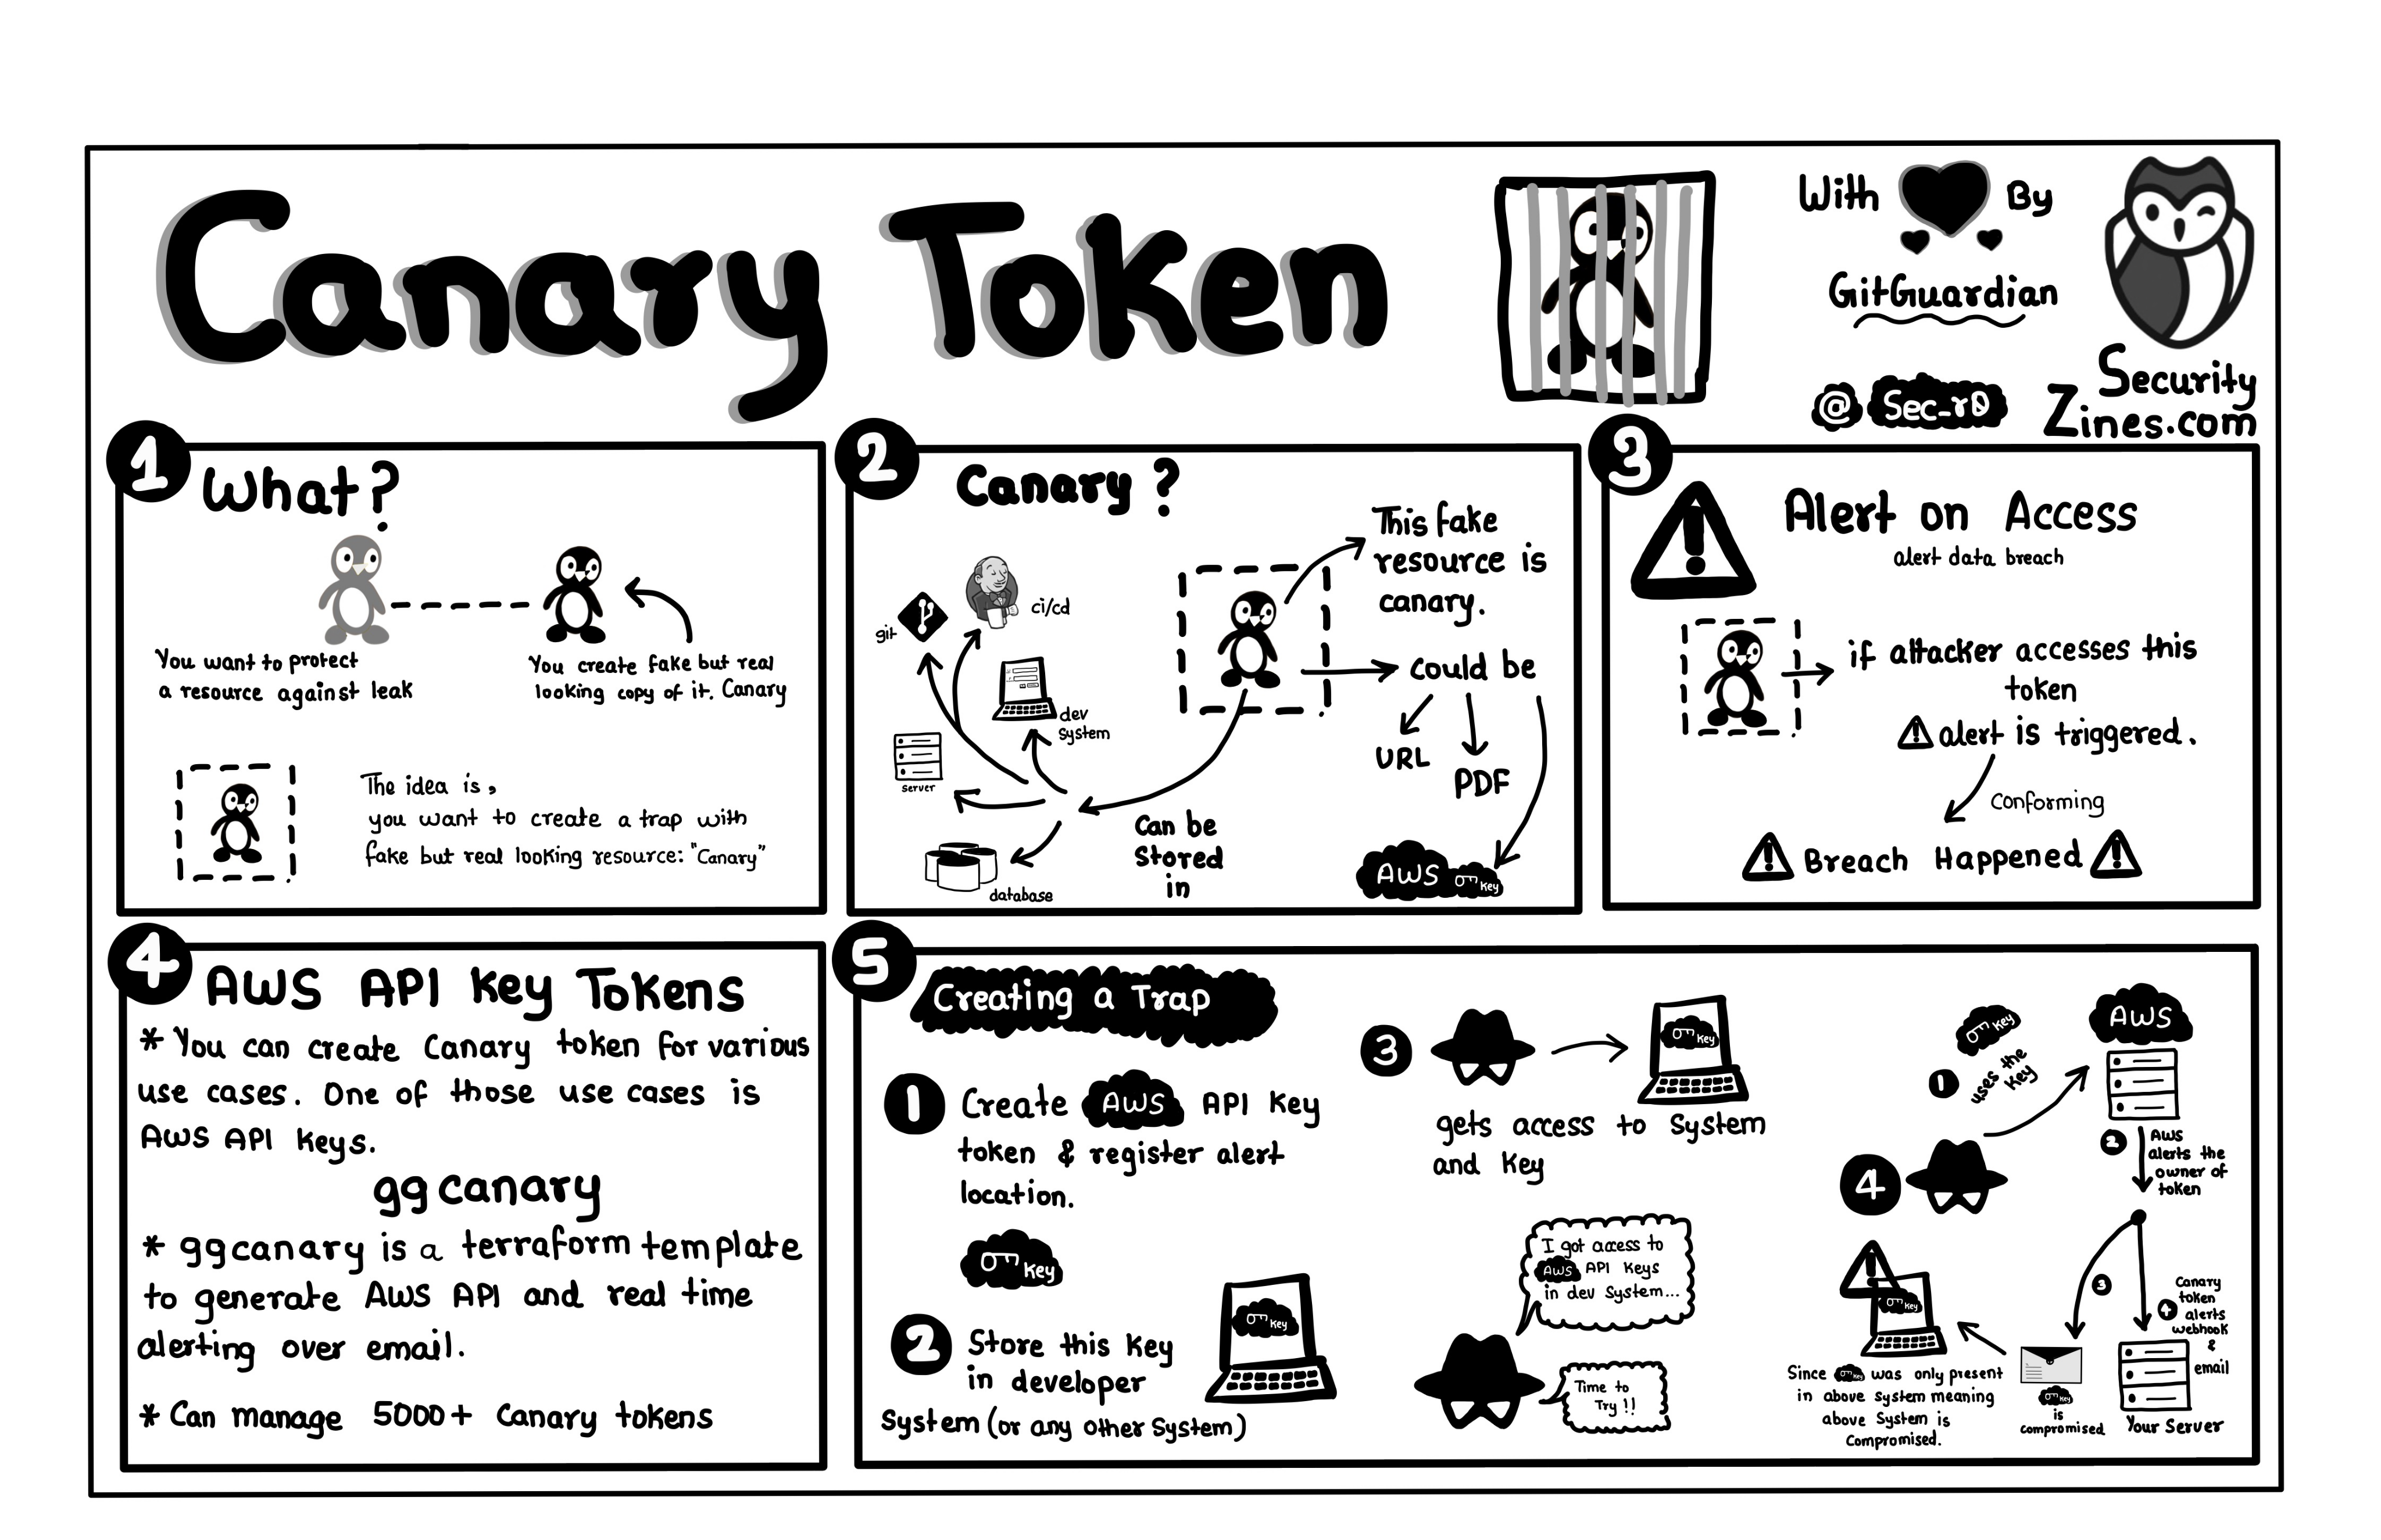
What Are Canary Tokens? Canary Tokens are unique identifiers embedded in files, URLs, or systems that act as early warning mechanisms for potential breaches. When an attacker accesses or interacts with these tokens, they trigger silent alerts, notifying the defender of unauthorized activity.
How They Work: These tokens mimic sensitive assets, such as fake credentials or API keys, strategically planted within repositories, emails, or logs. If someone tries to exploit or exfiltrate them, the token “calls home” to signal the breach, providing critical insight into the attacker's behavior.
Why Use Them? Canary Tokens help security teams detect breaches early, often before substantial damage occurs. They provide context, such as the method and intent of the attacker, allowing teams to respond swiftly to the intrusion.
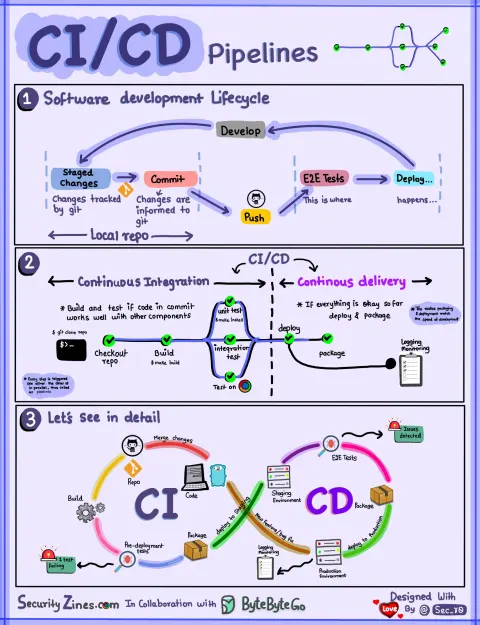
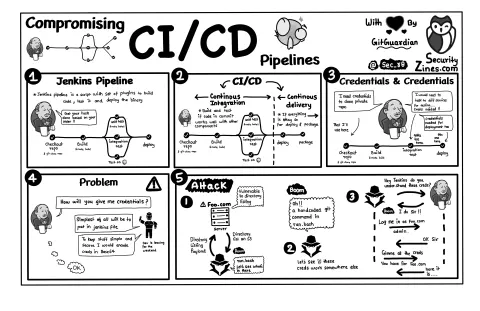
Common Use Cases: They can be embedded in private code repositories, cloud environments, CI/CD pipelines, or even fake database entries to monitor unauthorized access effectively. A practical example is planting a dummy AWS key within a private repository; if used, it immediately alerts the team.
With their stealth and simplicity, Canary Tokens are an invaluable addition to any organization’s defense strategy, equipping security professionals with real-time alerts and actionable insights.
This is the printer-friendly version. See the colour Canary Tokens flyer.