Every poster, sorted into six shelves.
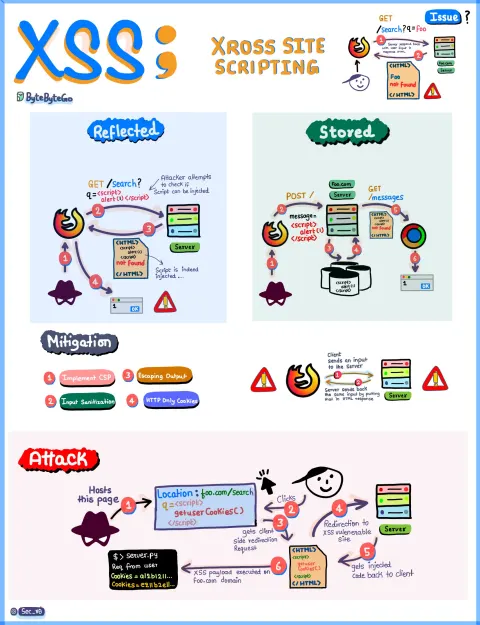
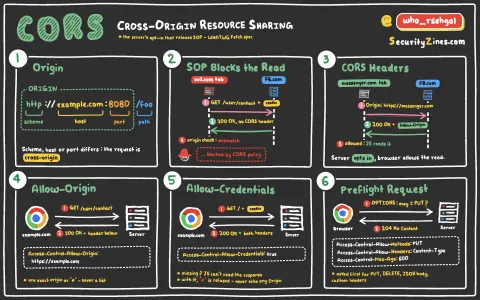
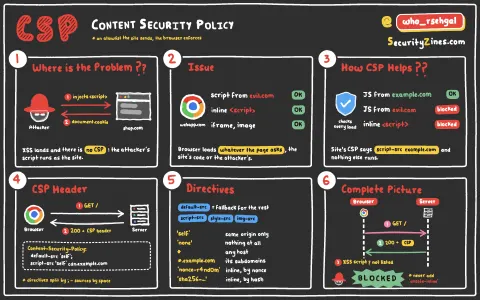
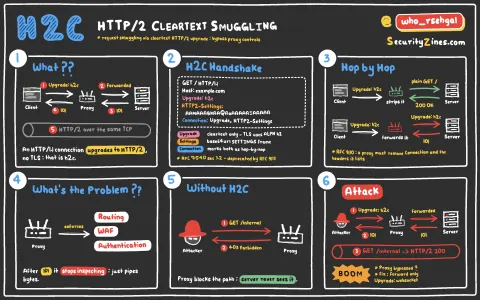
how browsers and web apps get attacked, and the controls that stop it
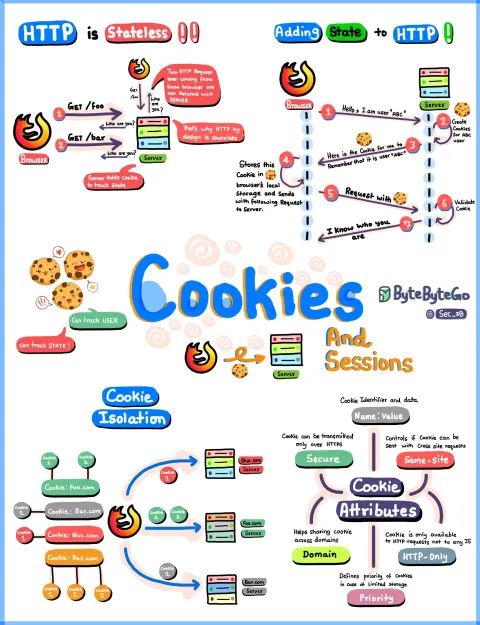
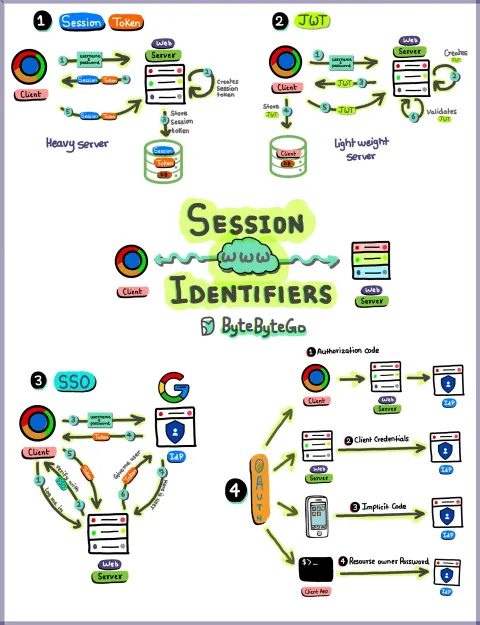
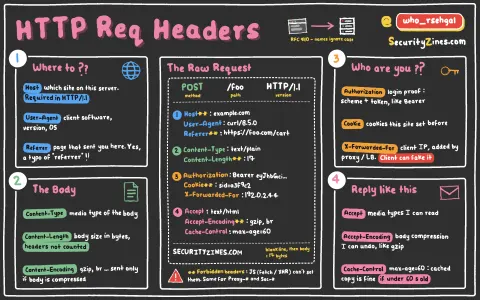
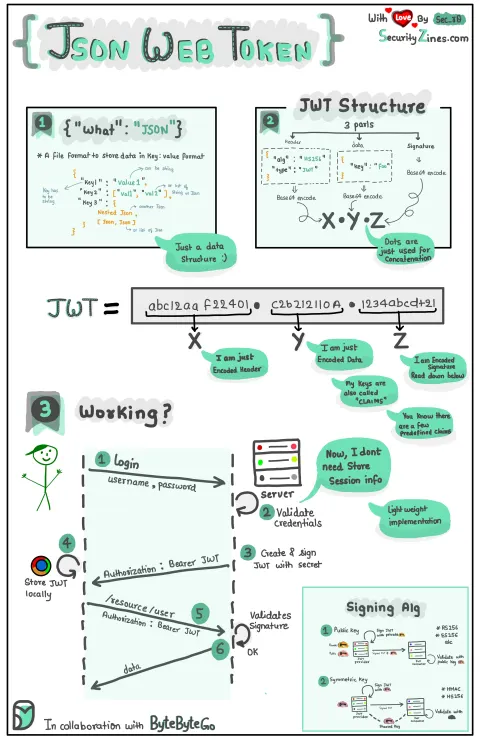
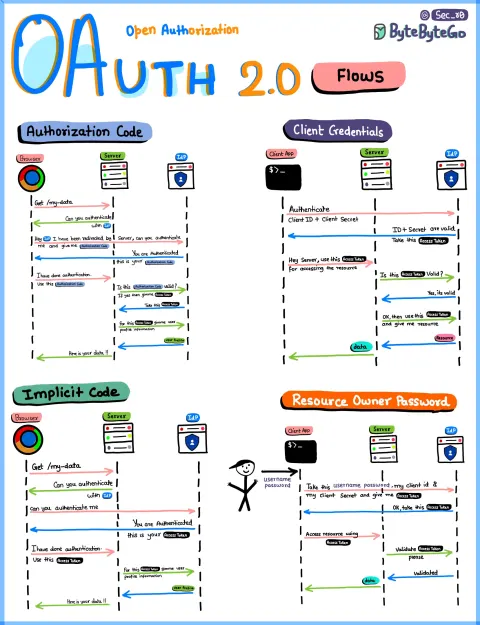
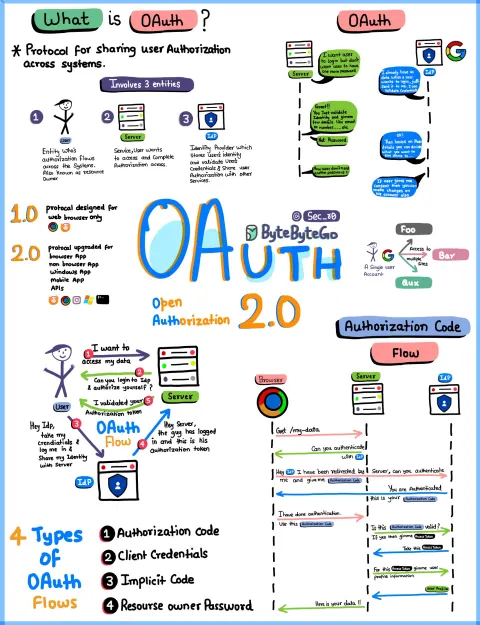
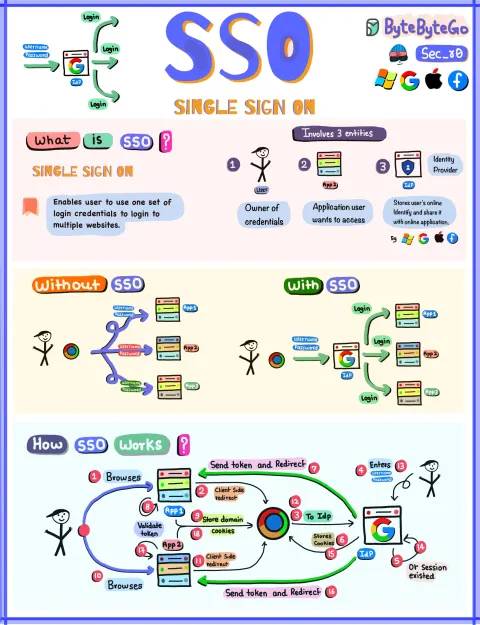
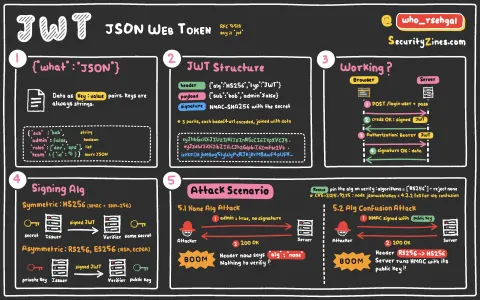
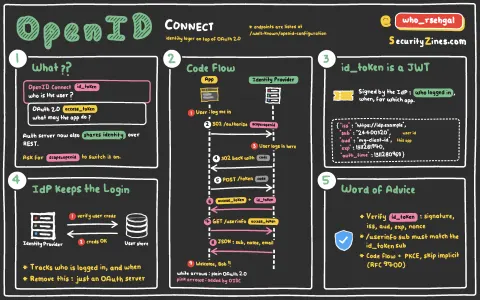
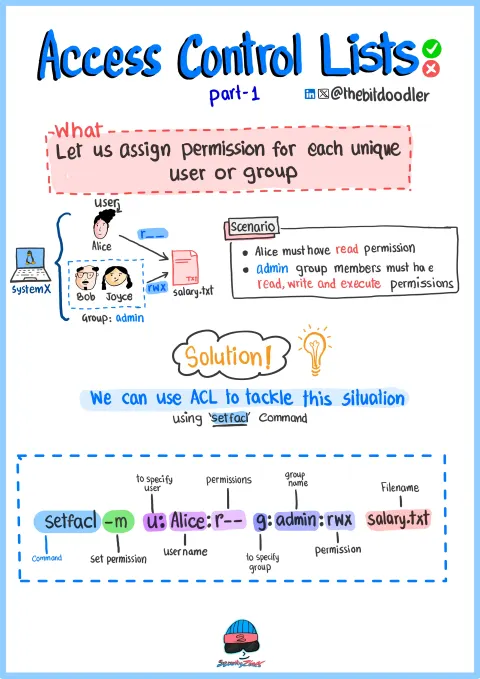
tokens, sessions, logins and who is allowed to do what
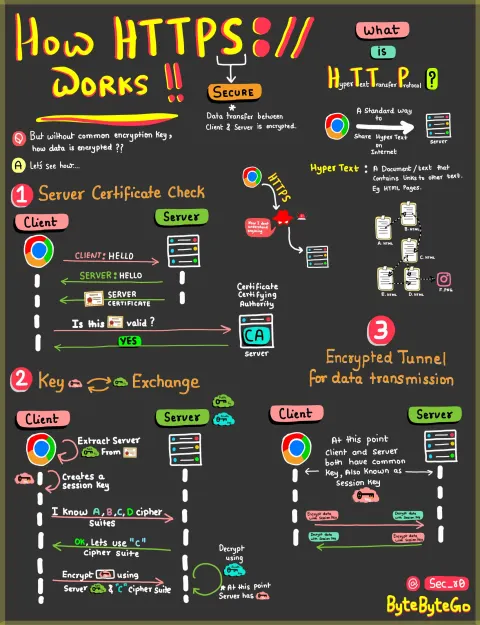
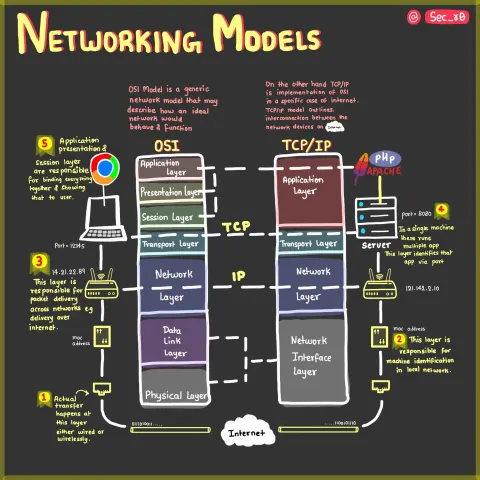
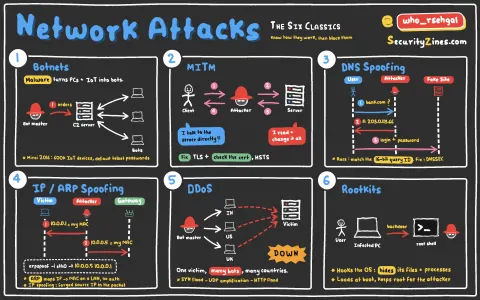
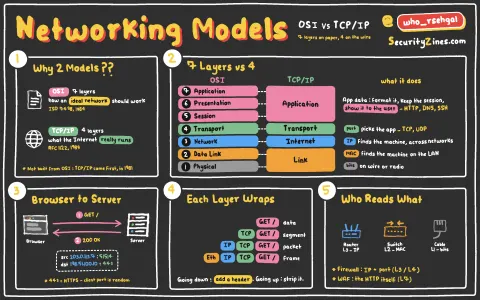
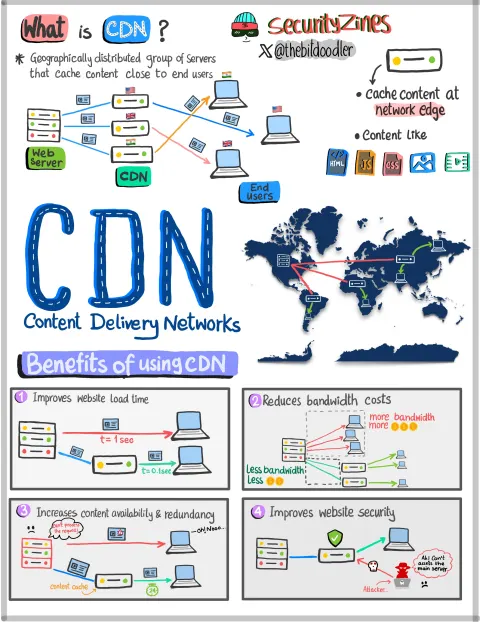
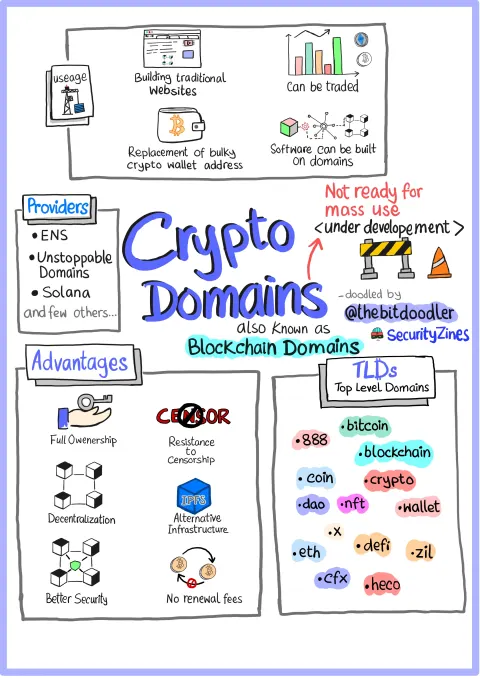
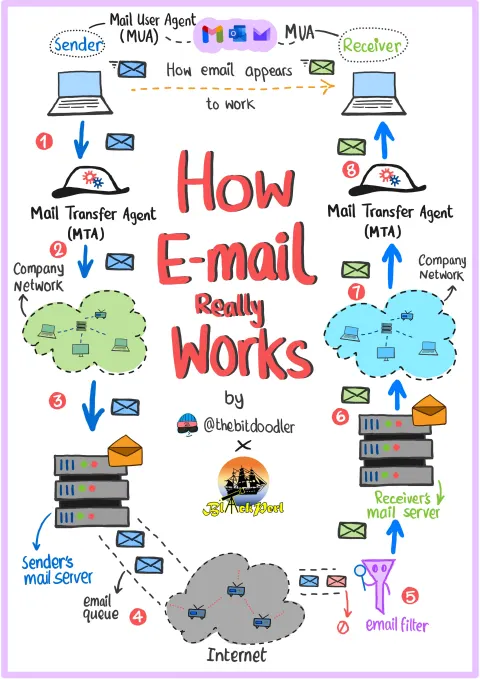
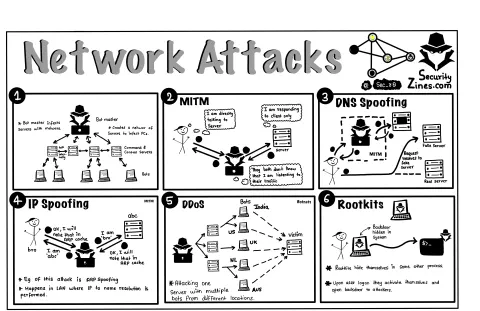
how packets, mail and domains actually travel
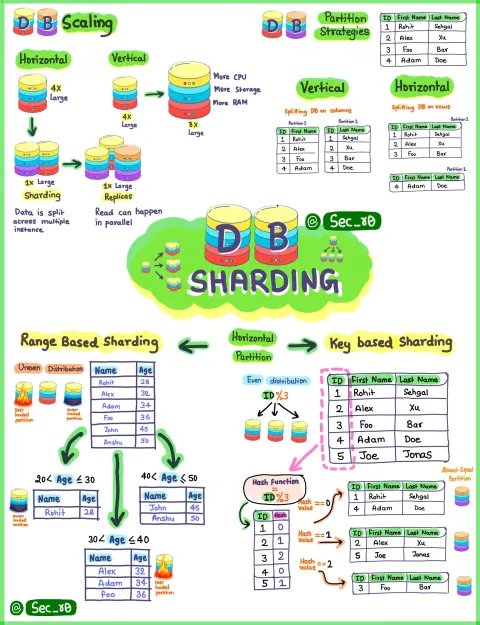
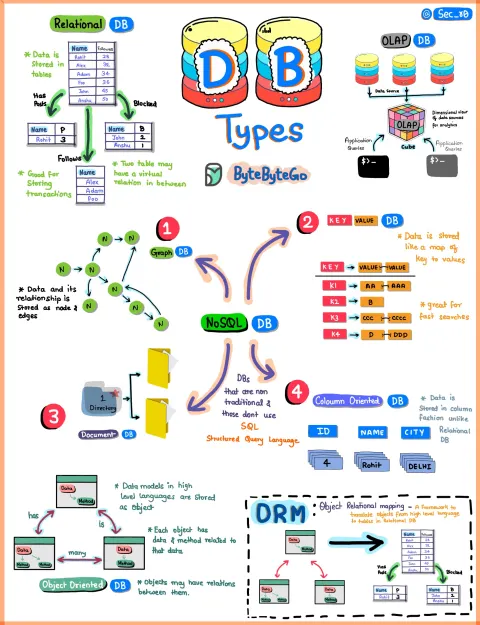
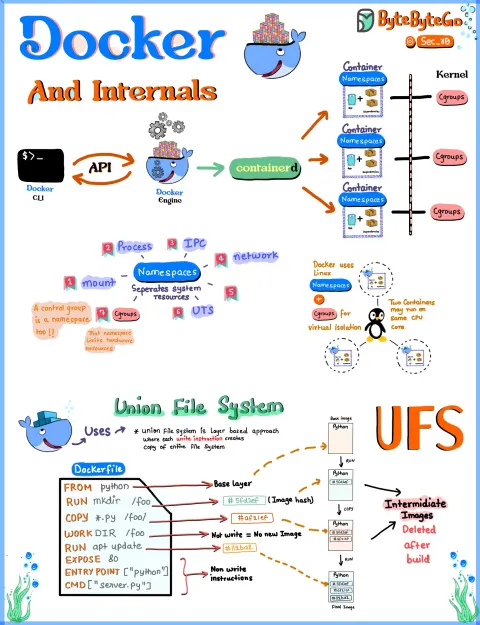
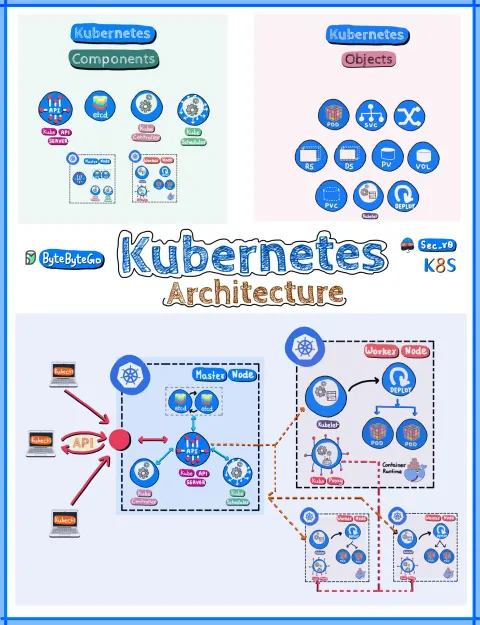
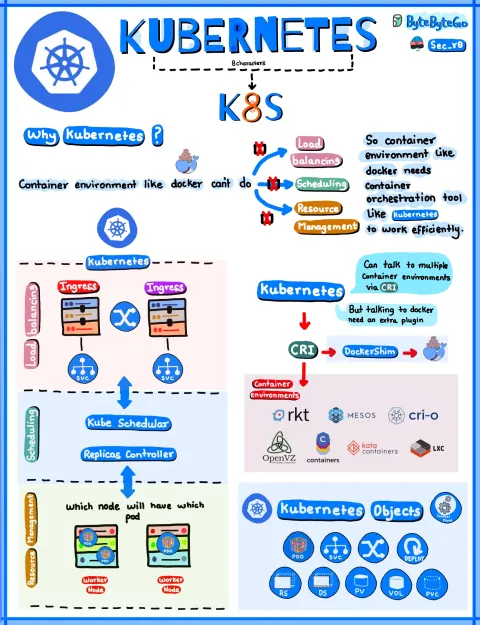
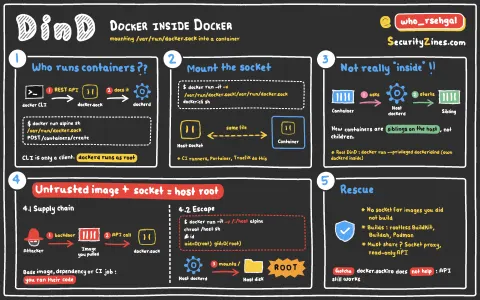
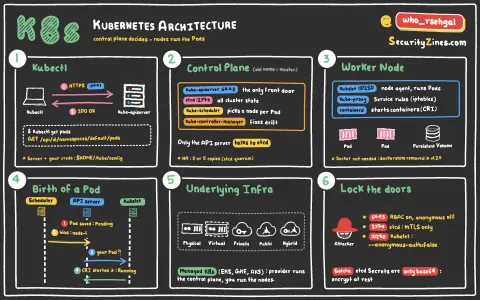
Docker, Kubernetes, infrastructure and data at scale
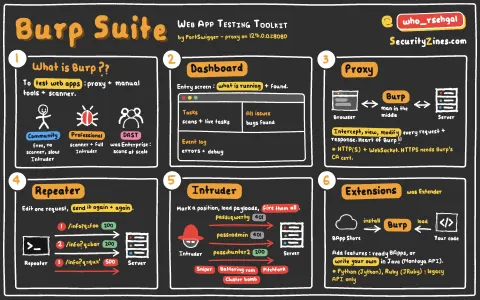
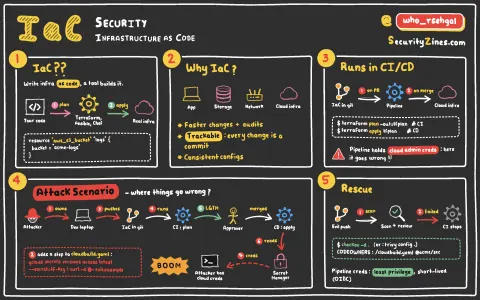
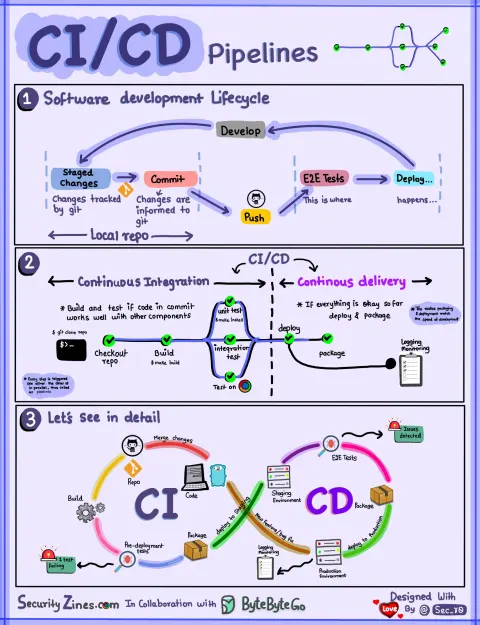
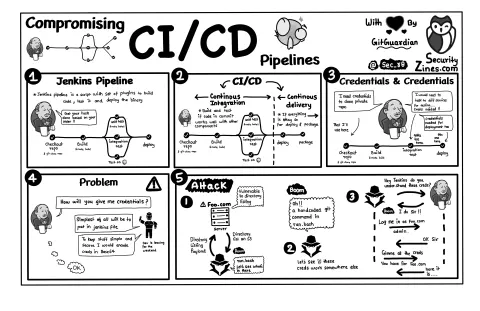
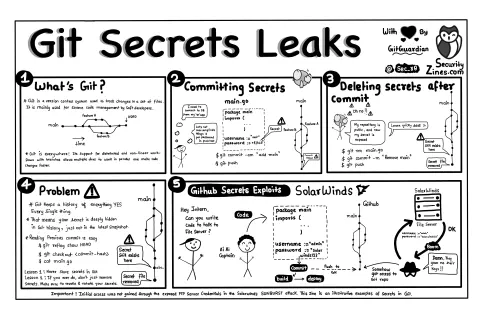
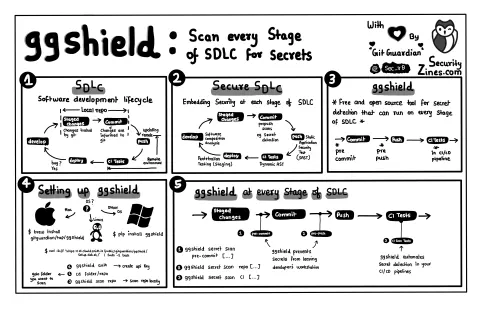
pipelines, secrets, tooling and thinking like an attacker
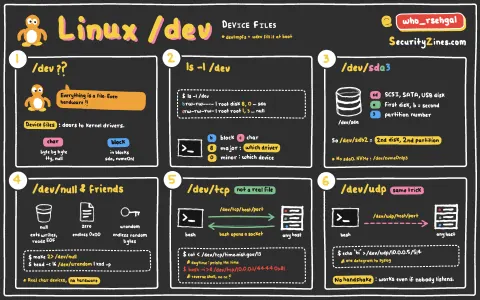
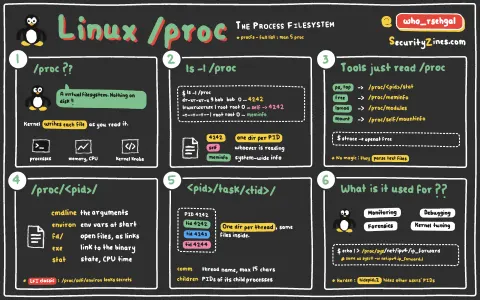
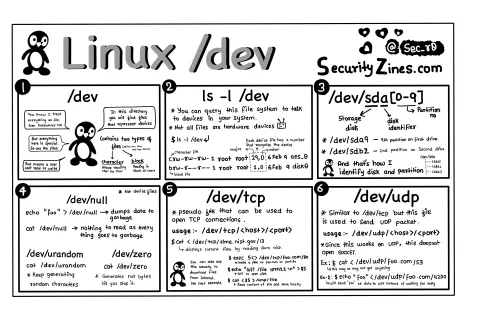
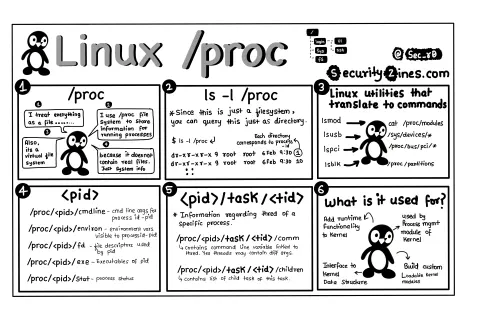
what lives under /dev and /proc
New posters land in the Security Zines newsletter on Substack. Free, no spam.
 SecurityZines.com