SecurityZines.com
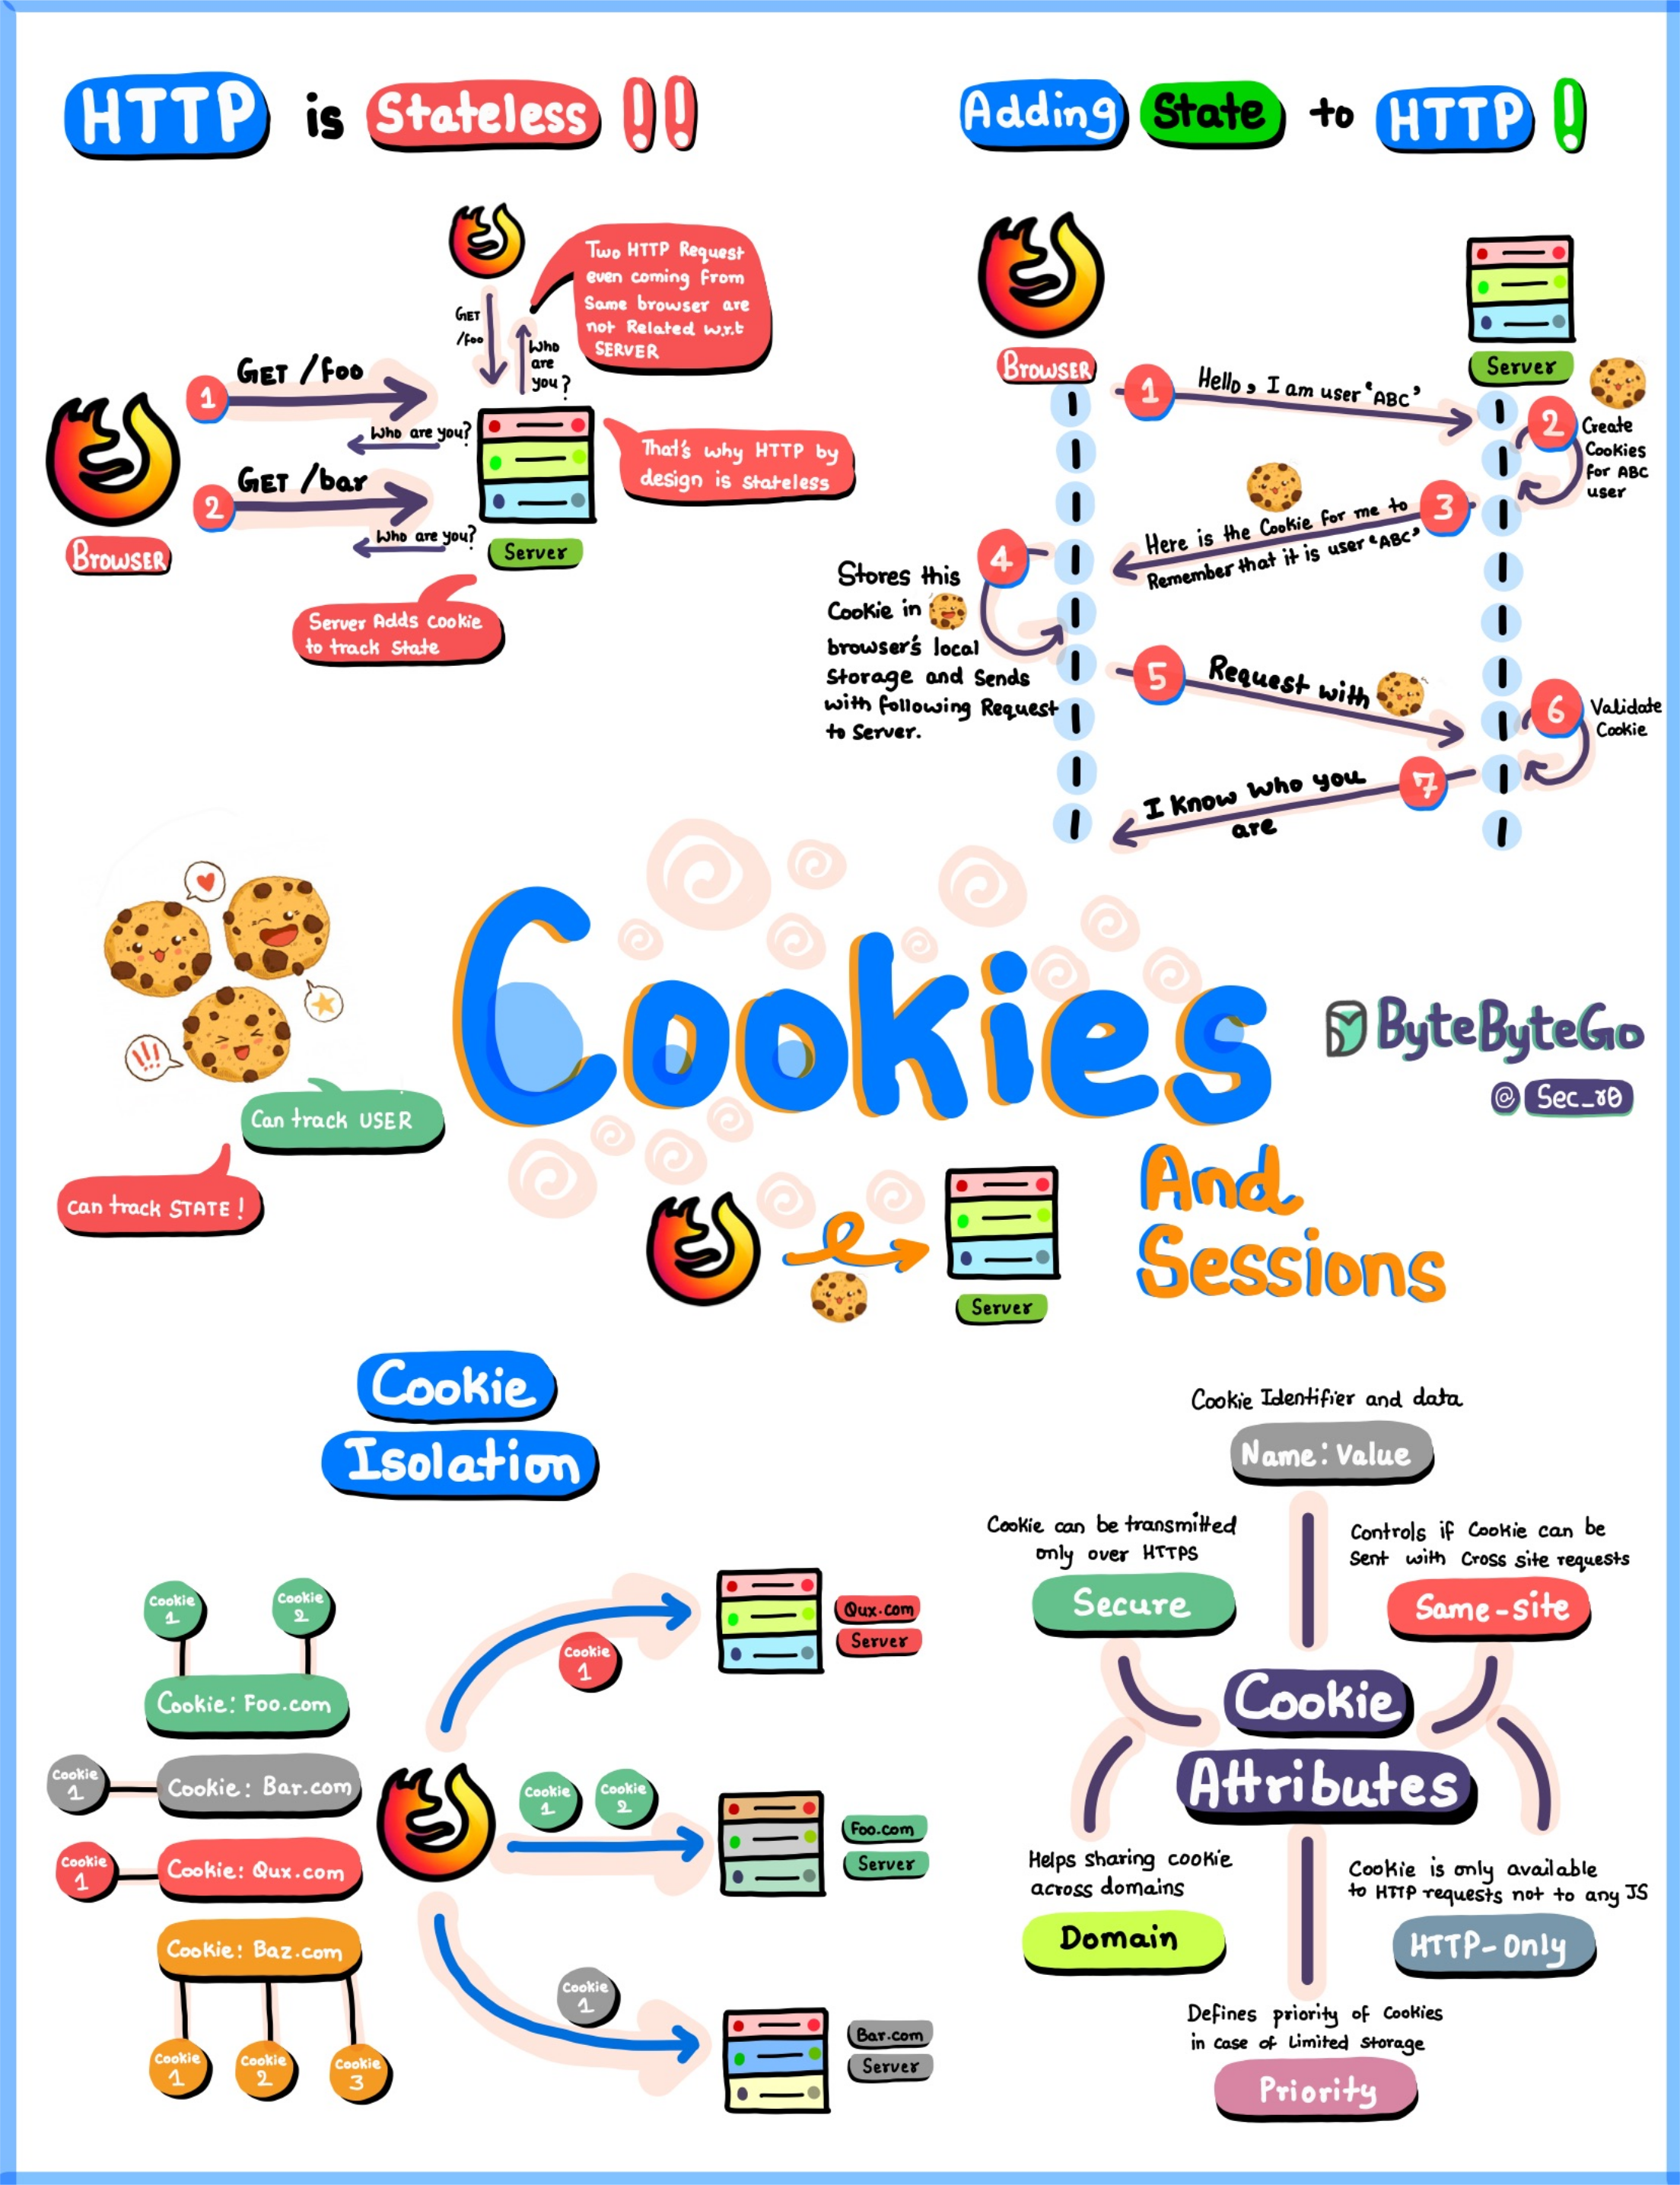
What it is: HTTP is stateless: two requests from the same browser look unrelated to the server. Cookies add state. The server sends a Set-Cookie header, the browser stores it, and sends it back on every later request to that site.
How sessions use it: the server creates a session, stores the user's data on its side, and hands the browser only a random session ID in a cookie. Each request carries the ID, and the server looks the session up.
Why it matters: whoever holds the session cookie is the user. Protect it with HttpOnly (no JavaScript access), Secure (HTTPS only) and SameSite (limits cross-site sending, which blunts CSRF), and rotate the ID at login.