SecurityZines.com
Web Security
35 free hand-drawn cheat sheets on how browsers and web apps get attacked, and the controls that stop it.
Visual explanations of how web applications are attacked and defended: XSS, CSRF, IDOR, SSTI, XXE, file inclusion, request smuggling and ReDoS, plus the browser controls that stop them (Same Origin Policy, CORS, CSP, cookies and HTTP headers) and Burp Suite for testing.
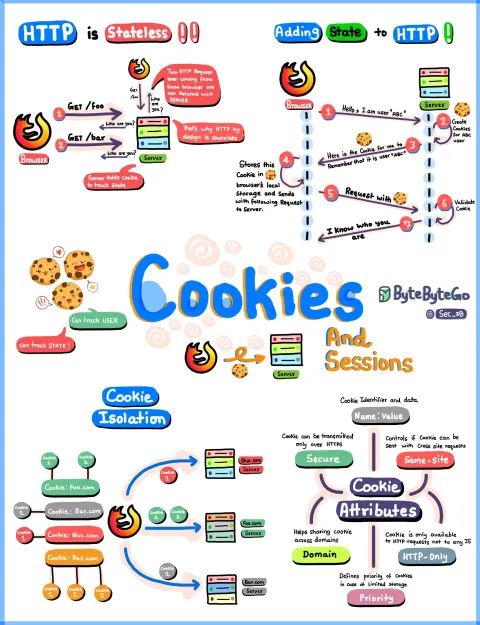
Cookies & Sessions
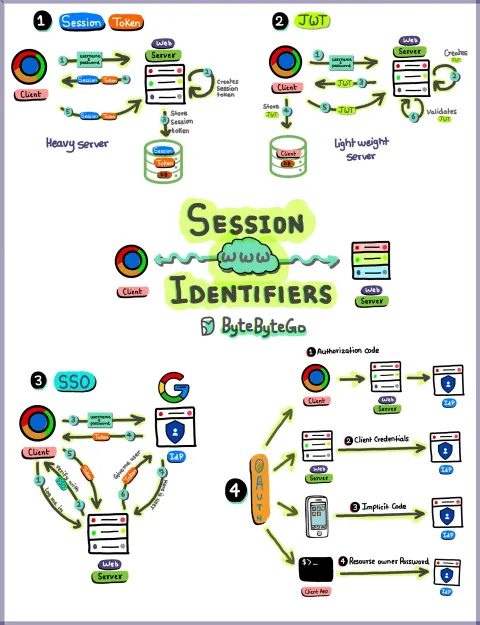
Session Identifiers
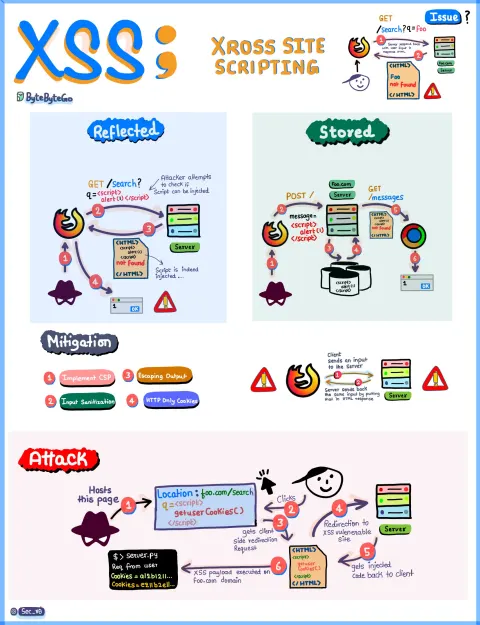
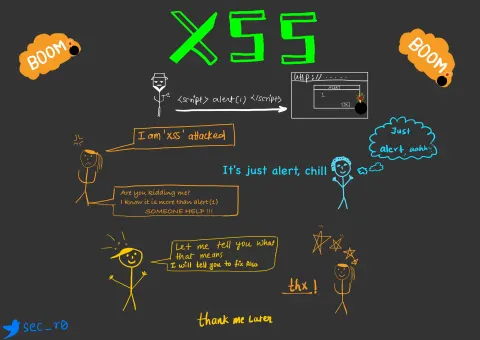
XSS
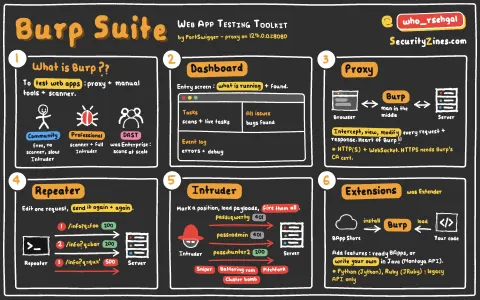
Burp Suite
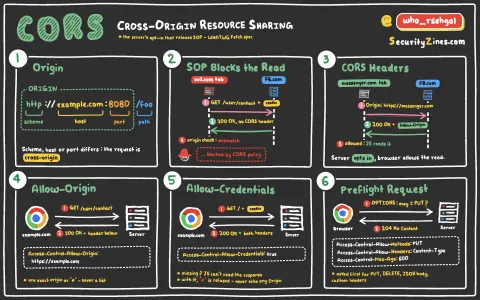
CORS
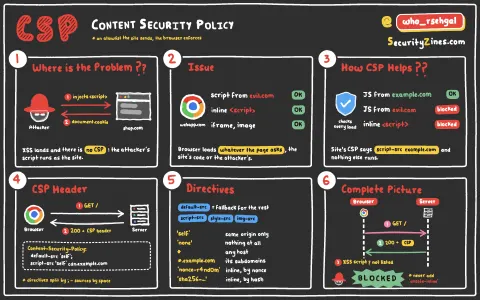
CSP
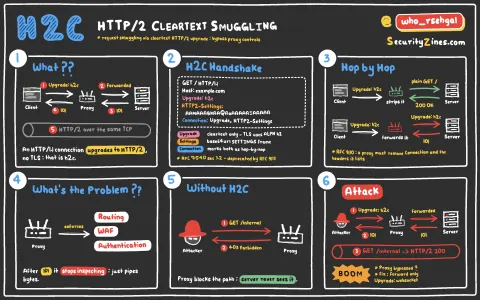
H2C Smuggling
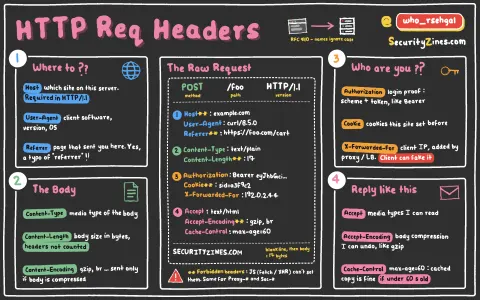
HTTP Request Headers
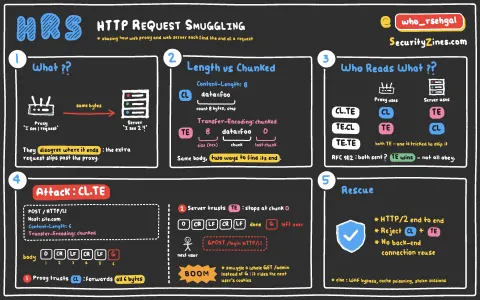
HTTP Request Smuggling
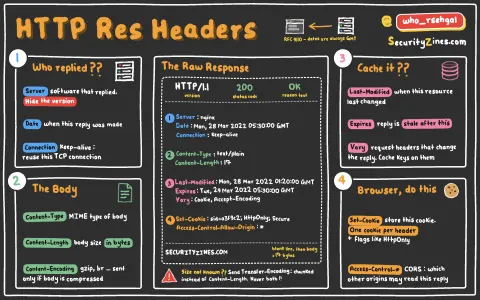
HTTP Response Headers
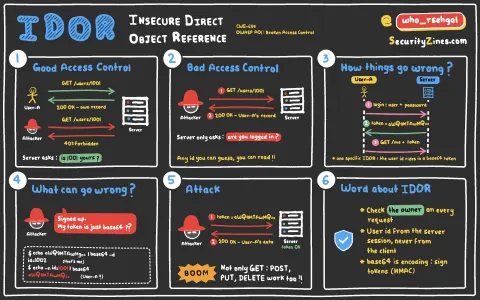
IDOR
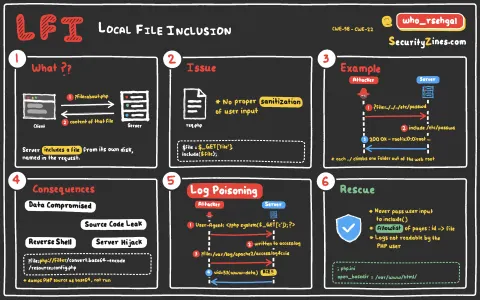
LFI
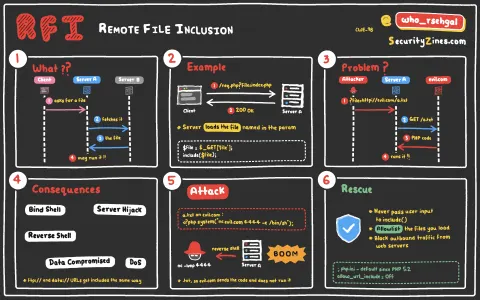
RFI
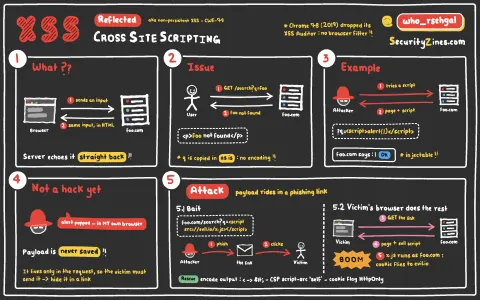
Reflected XSS
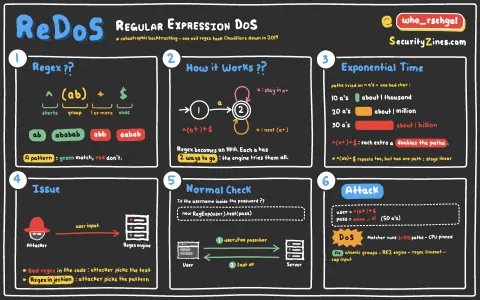
Regex DoS
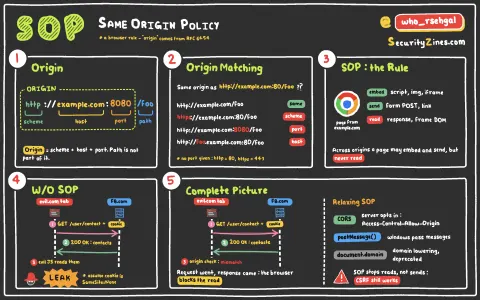
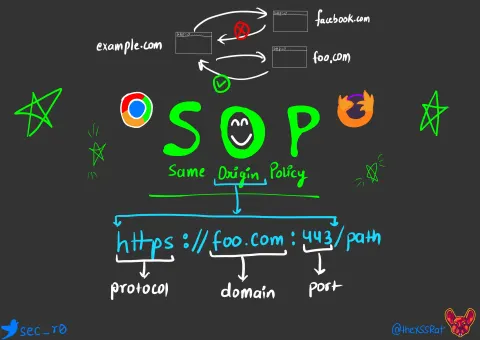
SOP
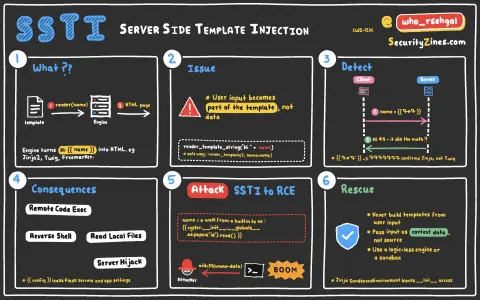
SSTI
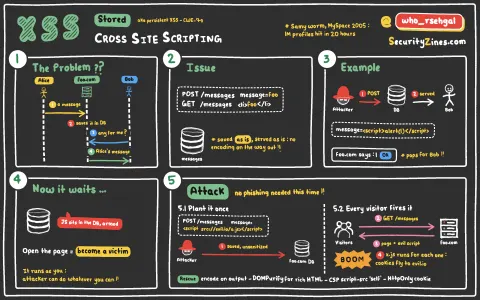
Stored XSS
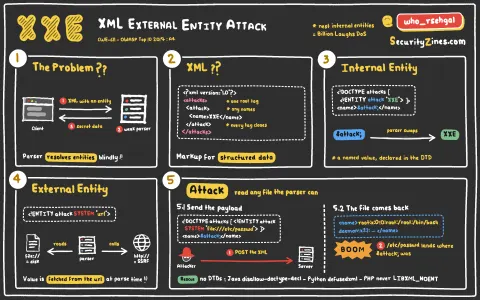
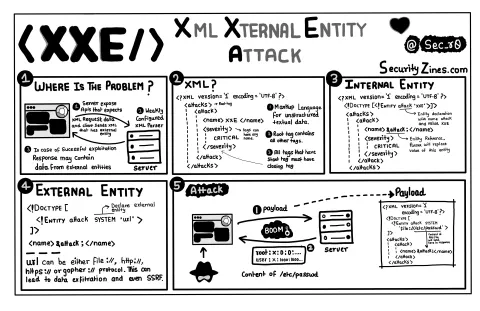
XXE
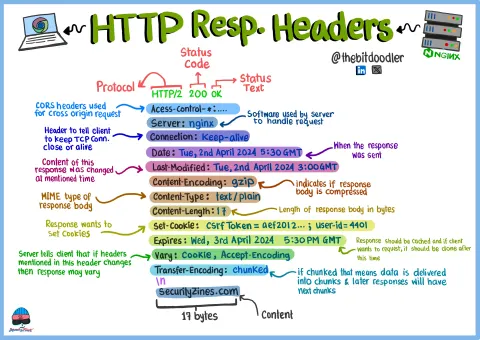
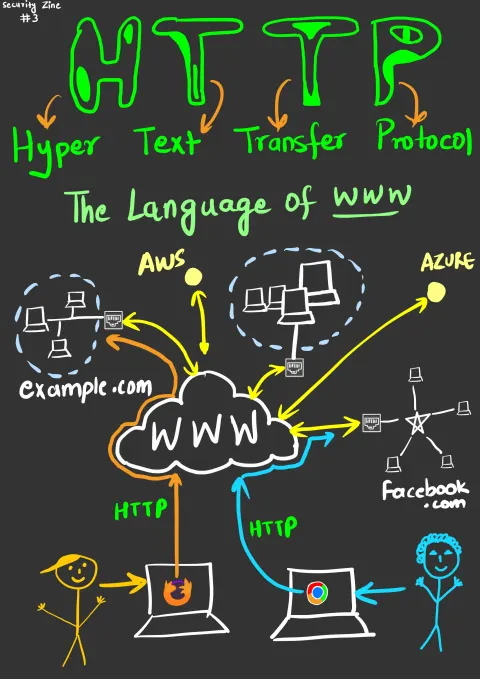
Understanding HTTP Response Headers
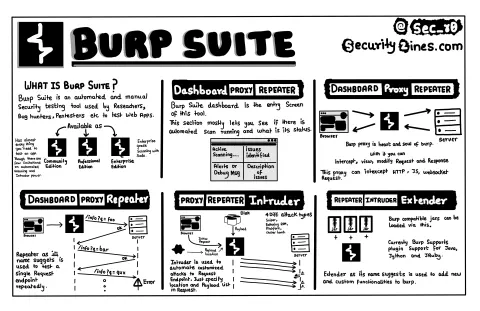
Burp Suite
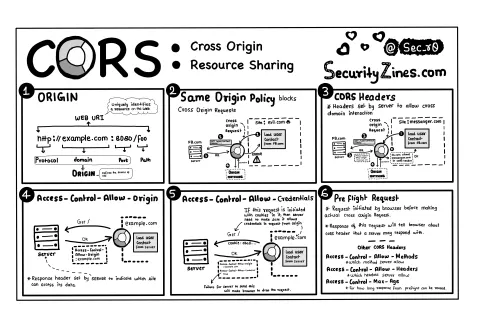
CORS
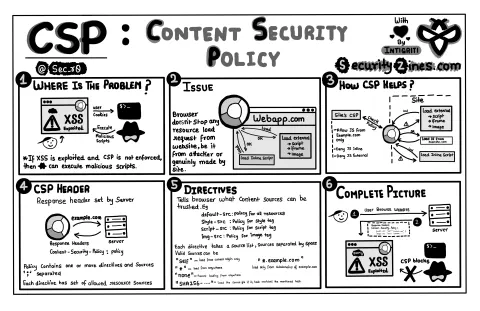
CSP
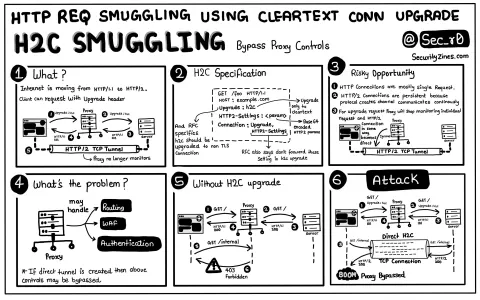
H2C Smuggling
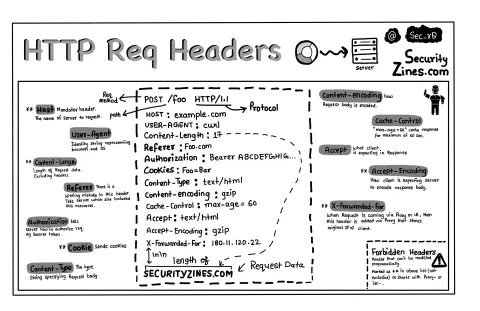
HTTP Request Headers
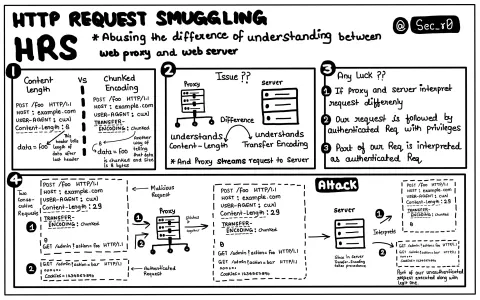
HTTP Request Smuggling
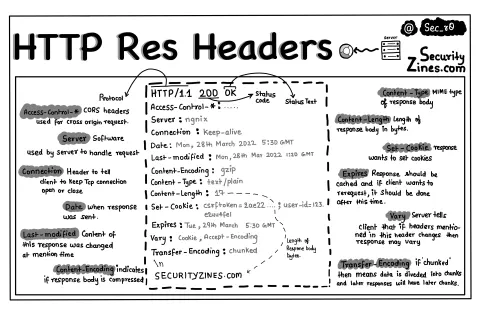
HTTP Response Headers
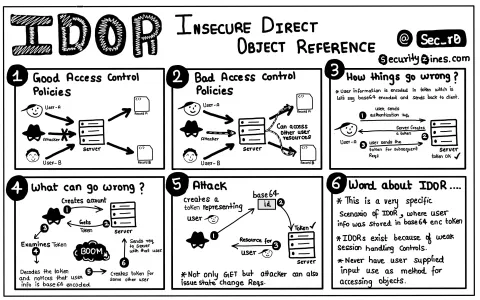
IDOR
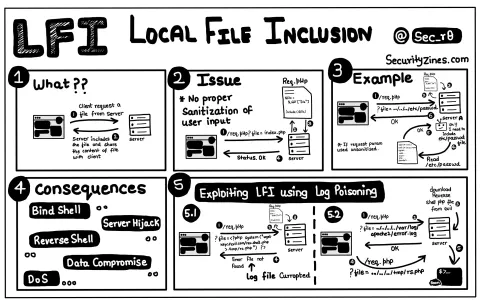
LFI
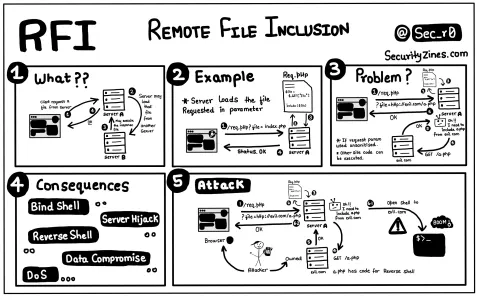
RFI
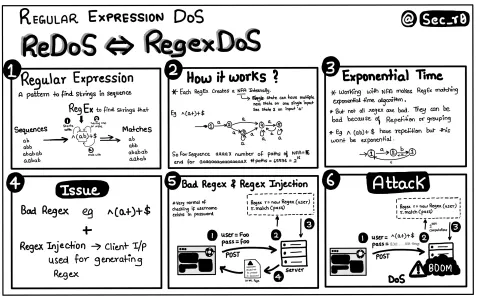
ReDoS
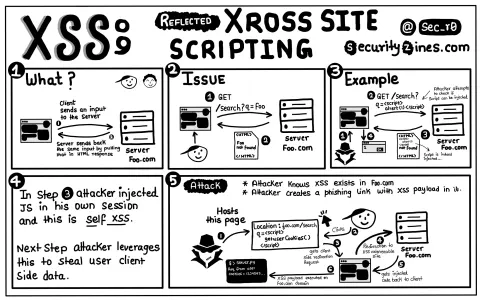
Reflected XSS
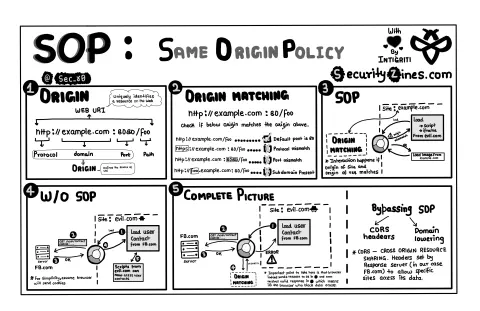
SOP
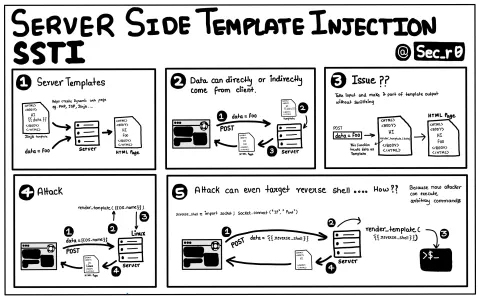
SSTI