SecurityZines.com
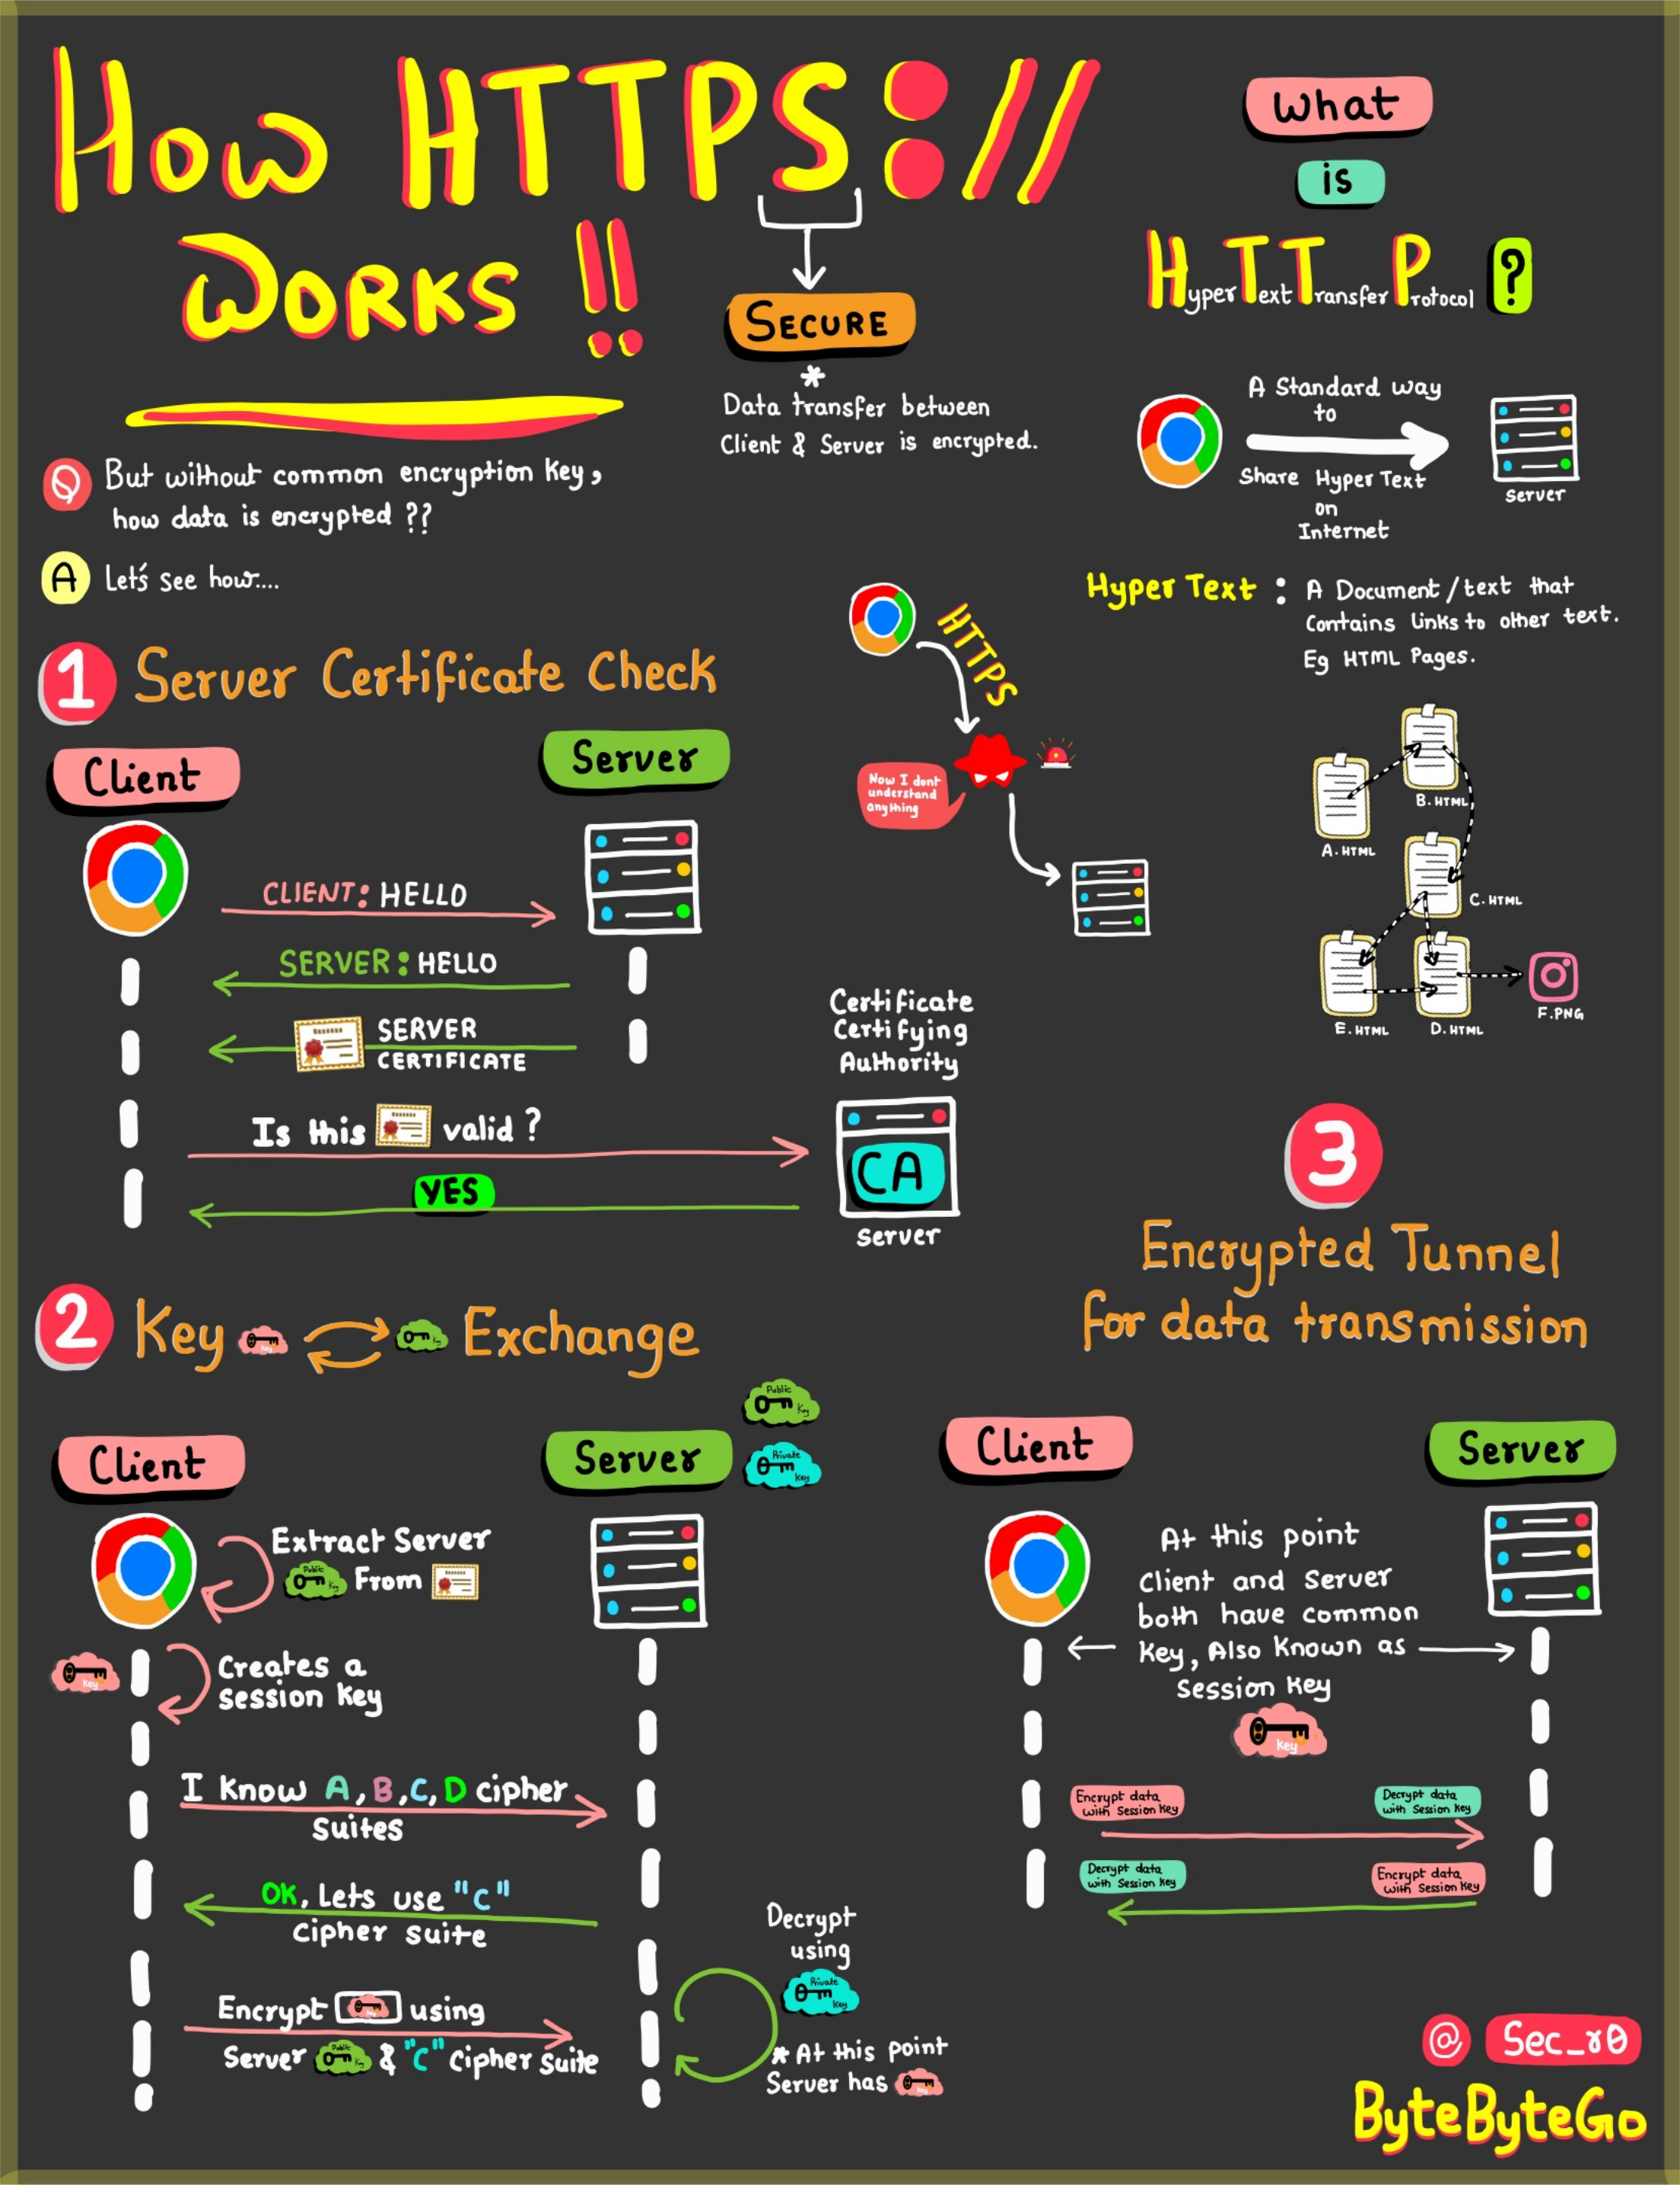
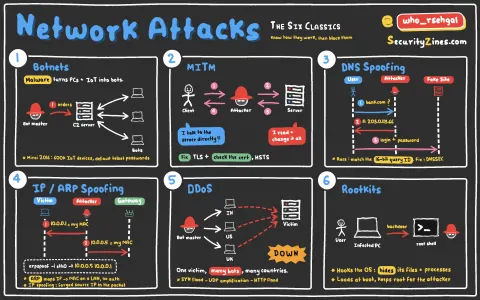
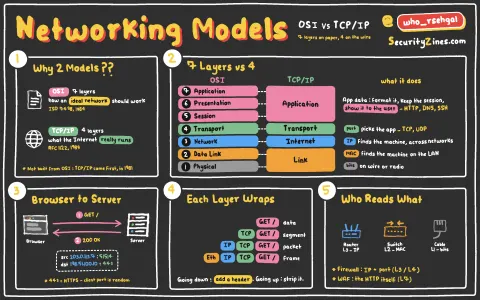
What it is: HTTPS is HTTP inside TLS. TLS gives three things: the server is who it claims (certificates), nobody can read the traffic (encryption), and nobody can change it unnoticed (integrity).
The handshake: the client says hello with the cipher suites it supports; the server answers with its certificate; the client checks that certificate chains to a trusted CA and matches the hostname; both sides run a key exchange (ECDHE in TLS 1.3) to agree on session keys that never cross the wire.
Why it matters: forward secrecy means a stolen server key cannot decrypt old traffic. HSTS stops downgrade to plain HTTP.