SecurityZines.com
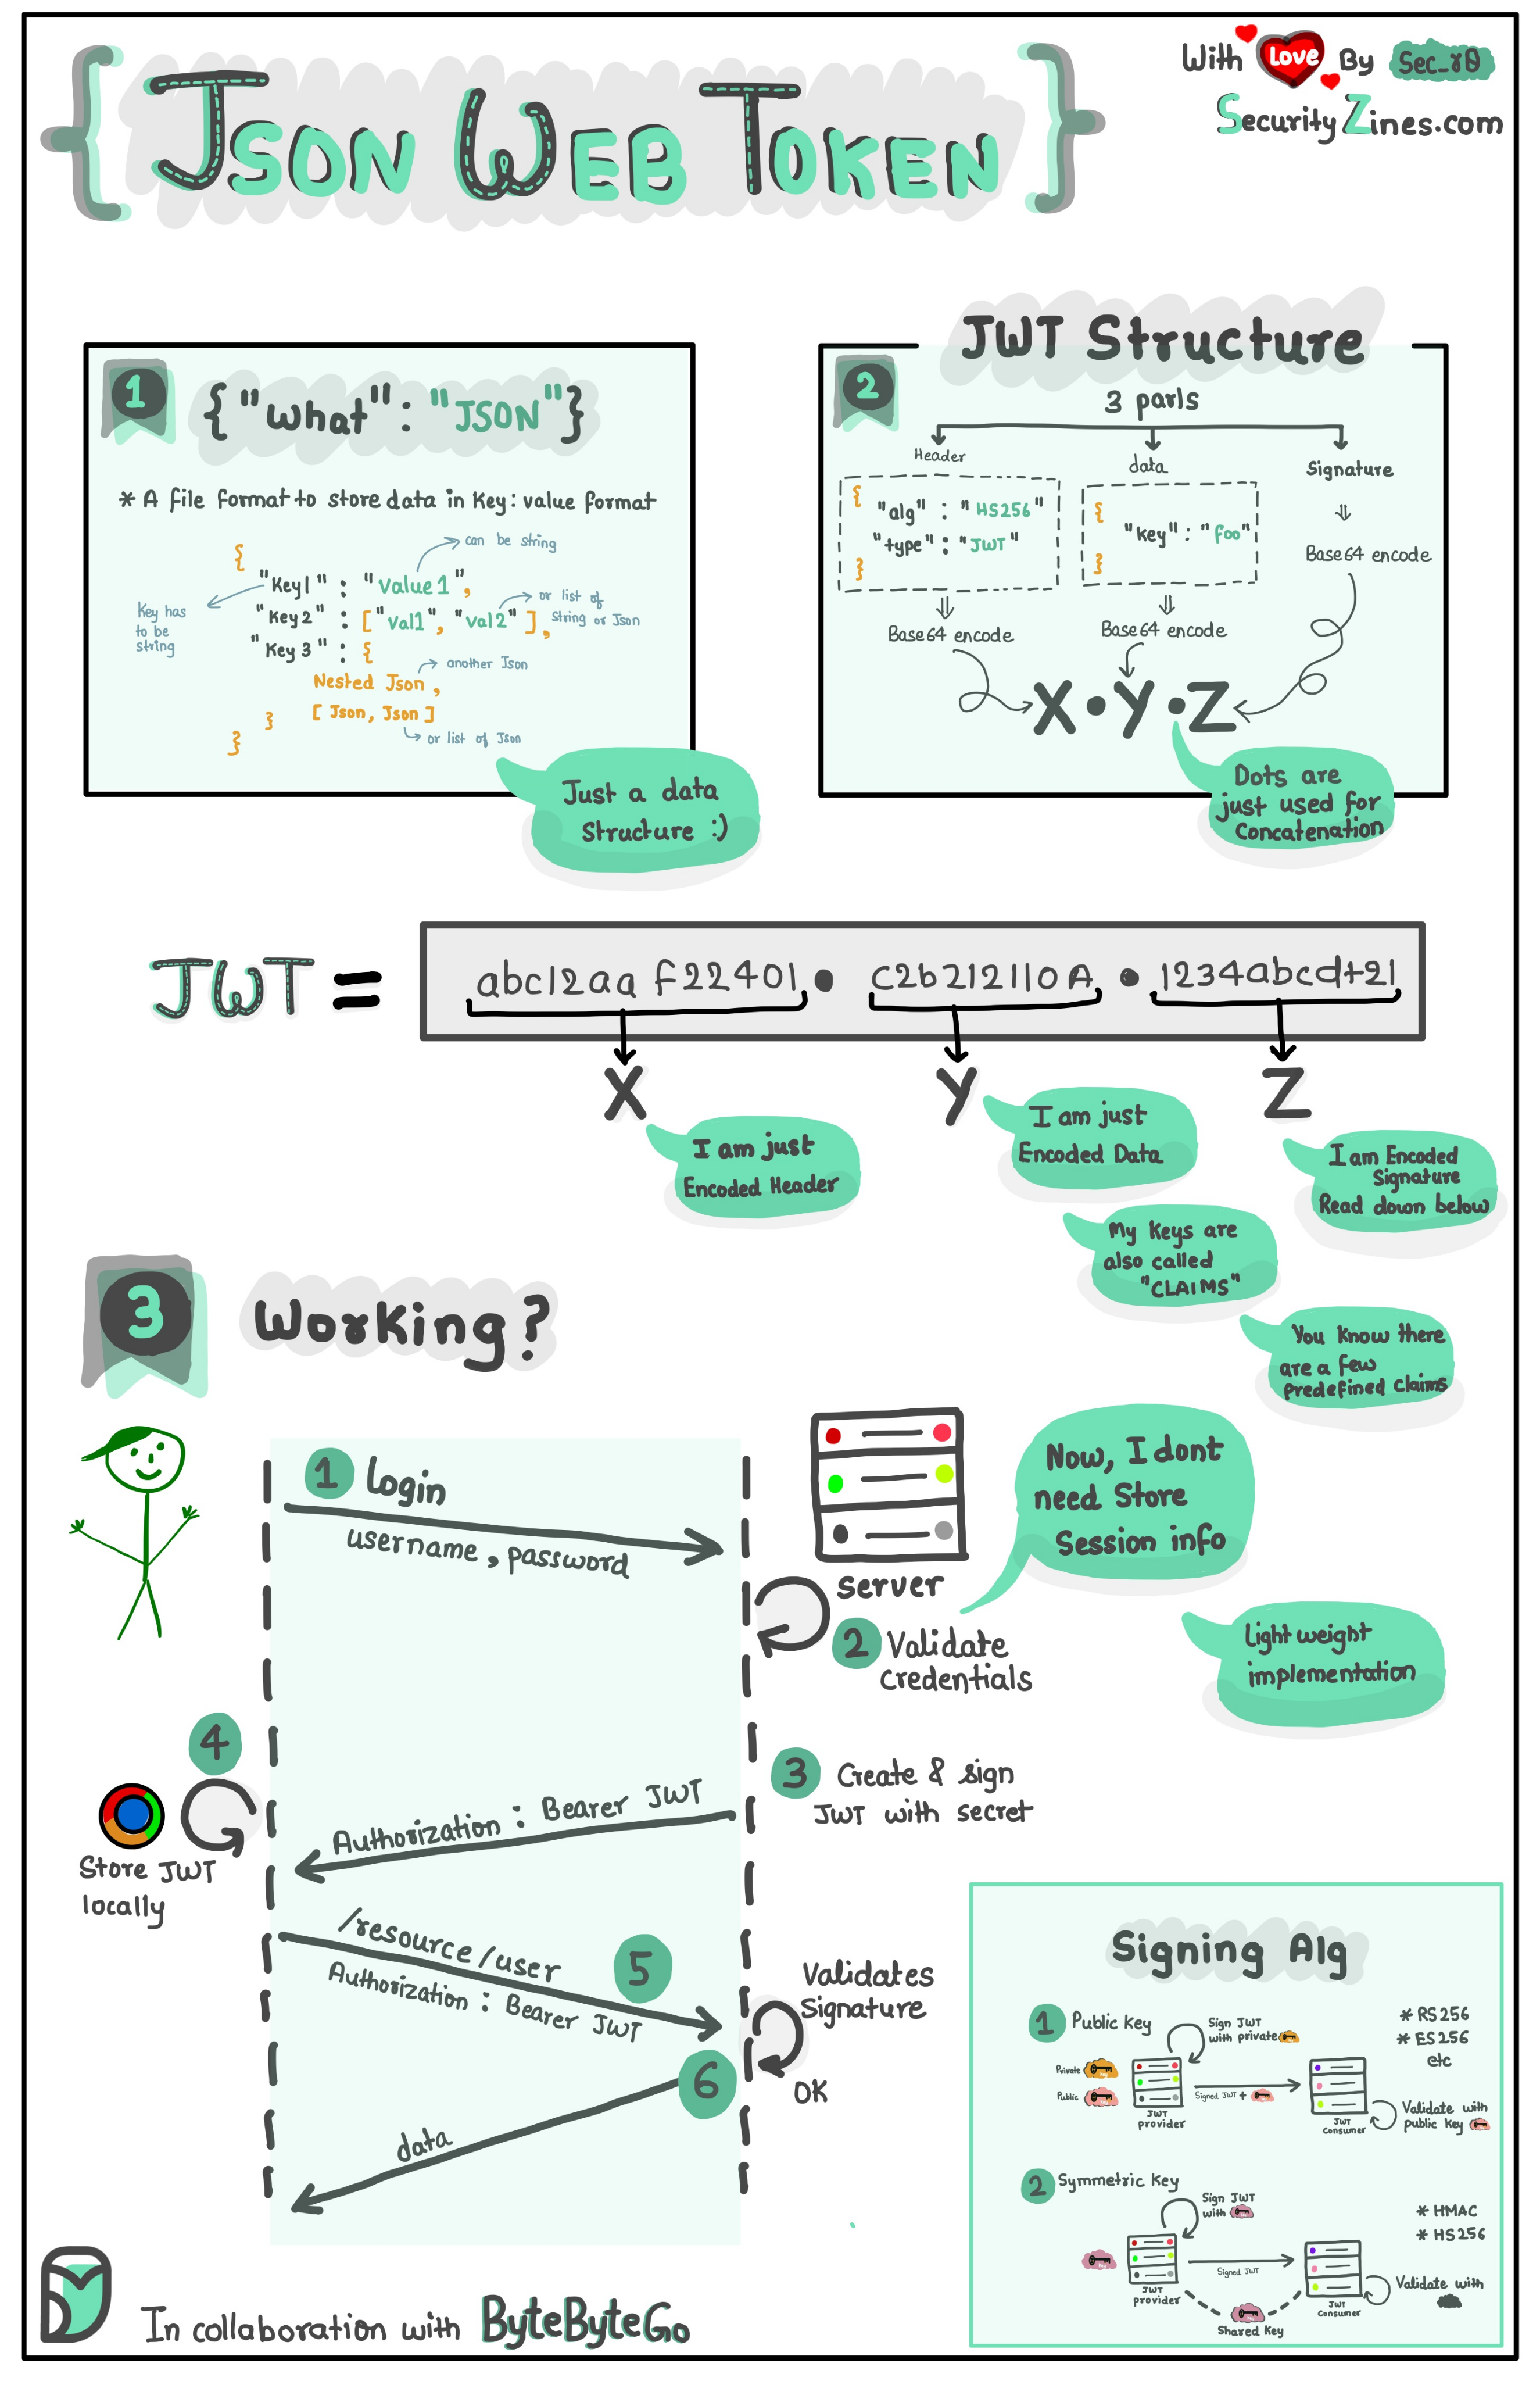
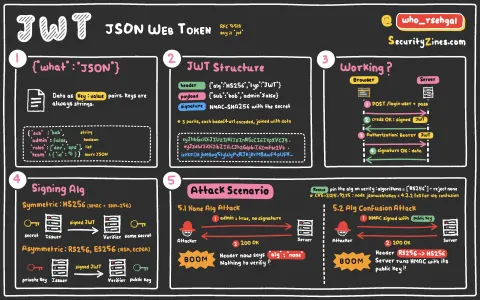
What it is: a JWT is three Base64URL parts joined by dots: a header (the algorithm), a payload (claims like sub, exp) and a signature over the first two. Anyone can read the payload; only the signature proves it was not changed.
How it is used: the server signs a token at login and the client sends it as Authorization: Bearer …. The server verifies the signature and expiry, with no session lookup.
Classic attacks: accepting alg: none, algorithm confusion (an RS256 public key used as an HS256 secret), weak HMAC secrets, and missing expiry checks. Pin the algorithm, validate exp, aud and iss, and keep tokens short-lived.