SecurityZines.com
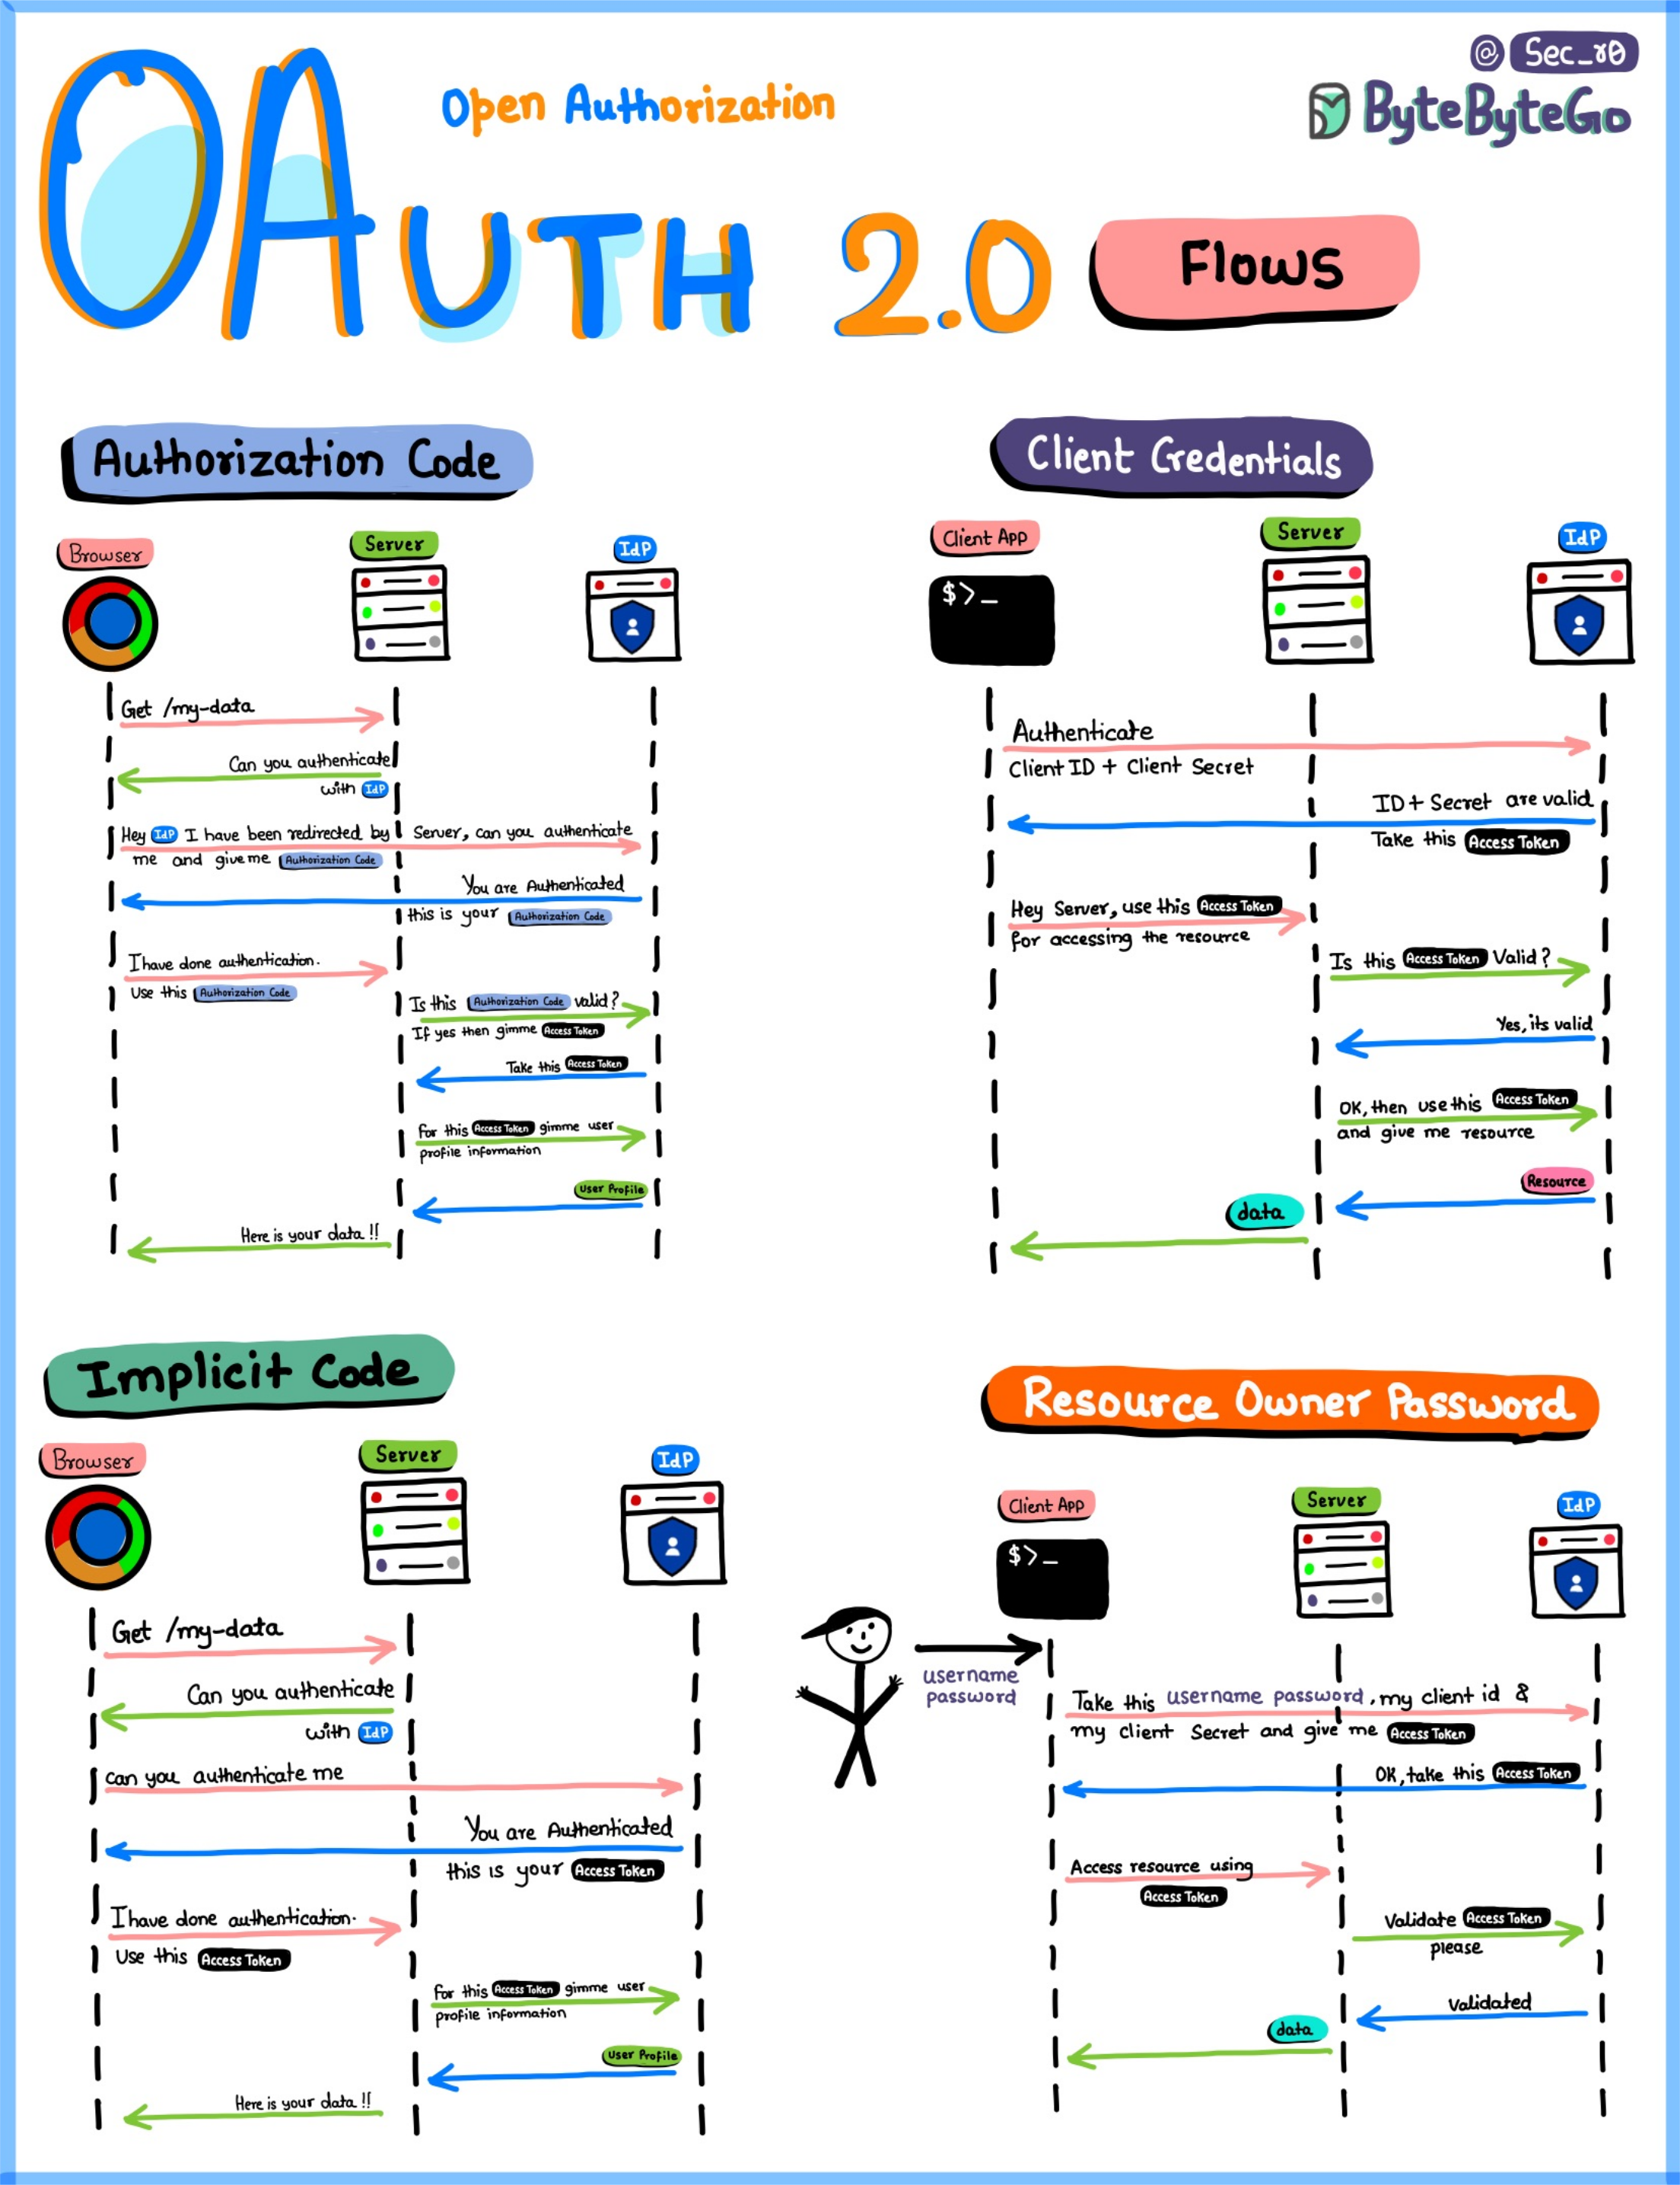
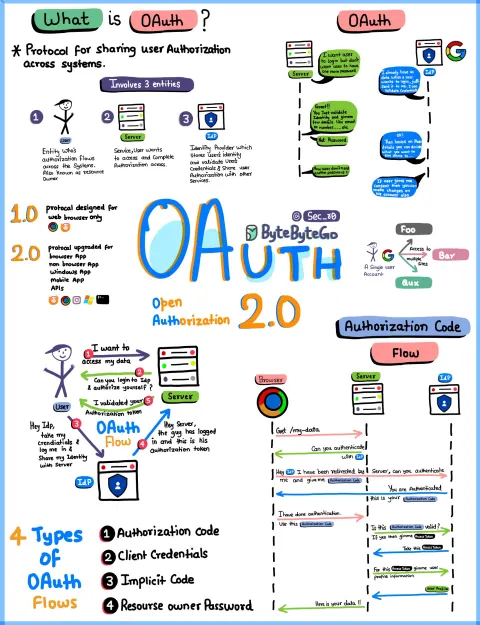
Authorization Code: the browser gets a short-lived code, and the app's backend swaps it for tokens. Add PKCE so a stolen code is useless; PKCE is now recommended for every client, including mobile and single-page apps.
Client Credentials: machine-to-machine. No user involved; the service authenticates with its own secret.
Device Code: for TVs and CLIs that cannot open a browser: the user approves on another device.
Avoid: the Implicit flow (tokens in the URL) and the Resource Owner Password flow (the app sees the password). The OAuth 2.1 draft drops both.