SecurityZines.com
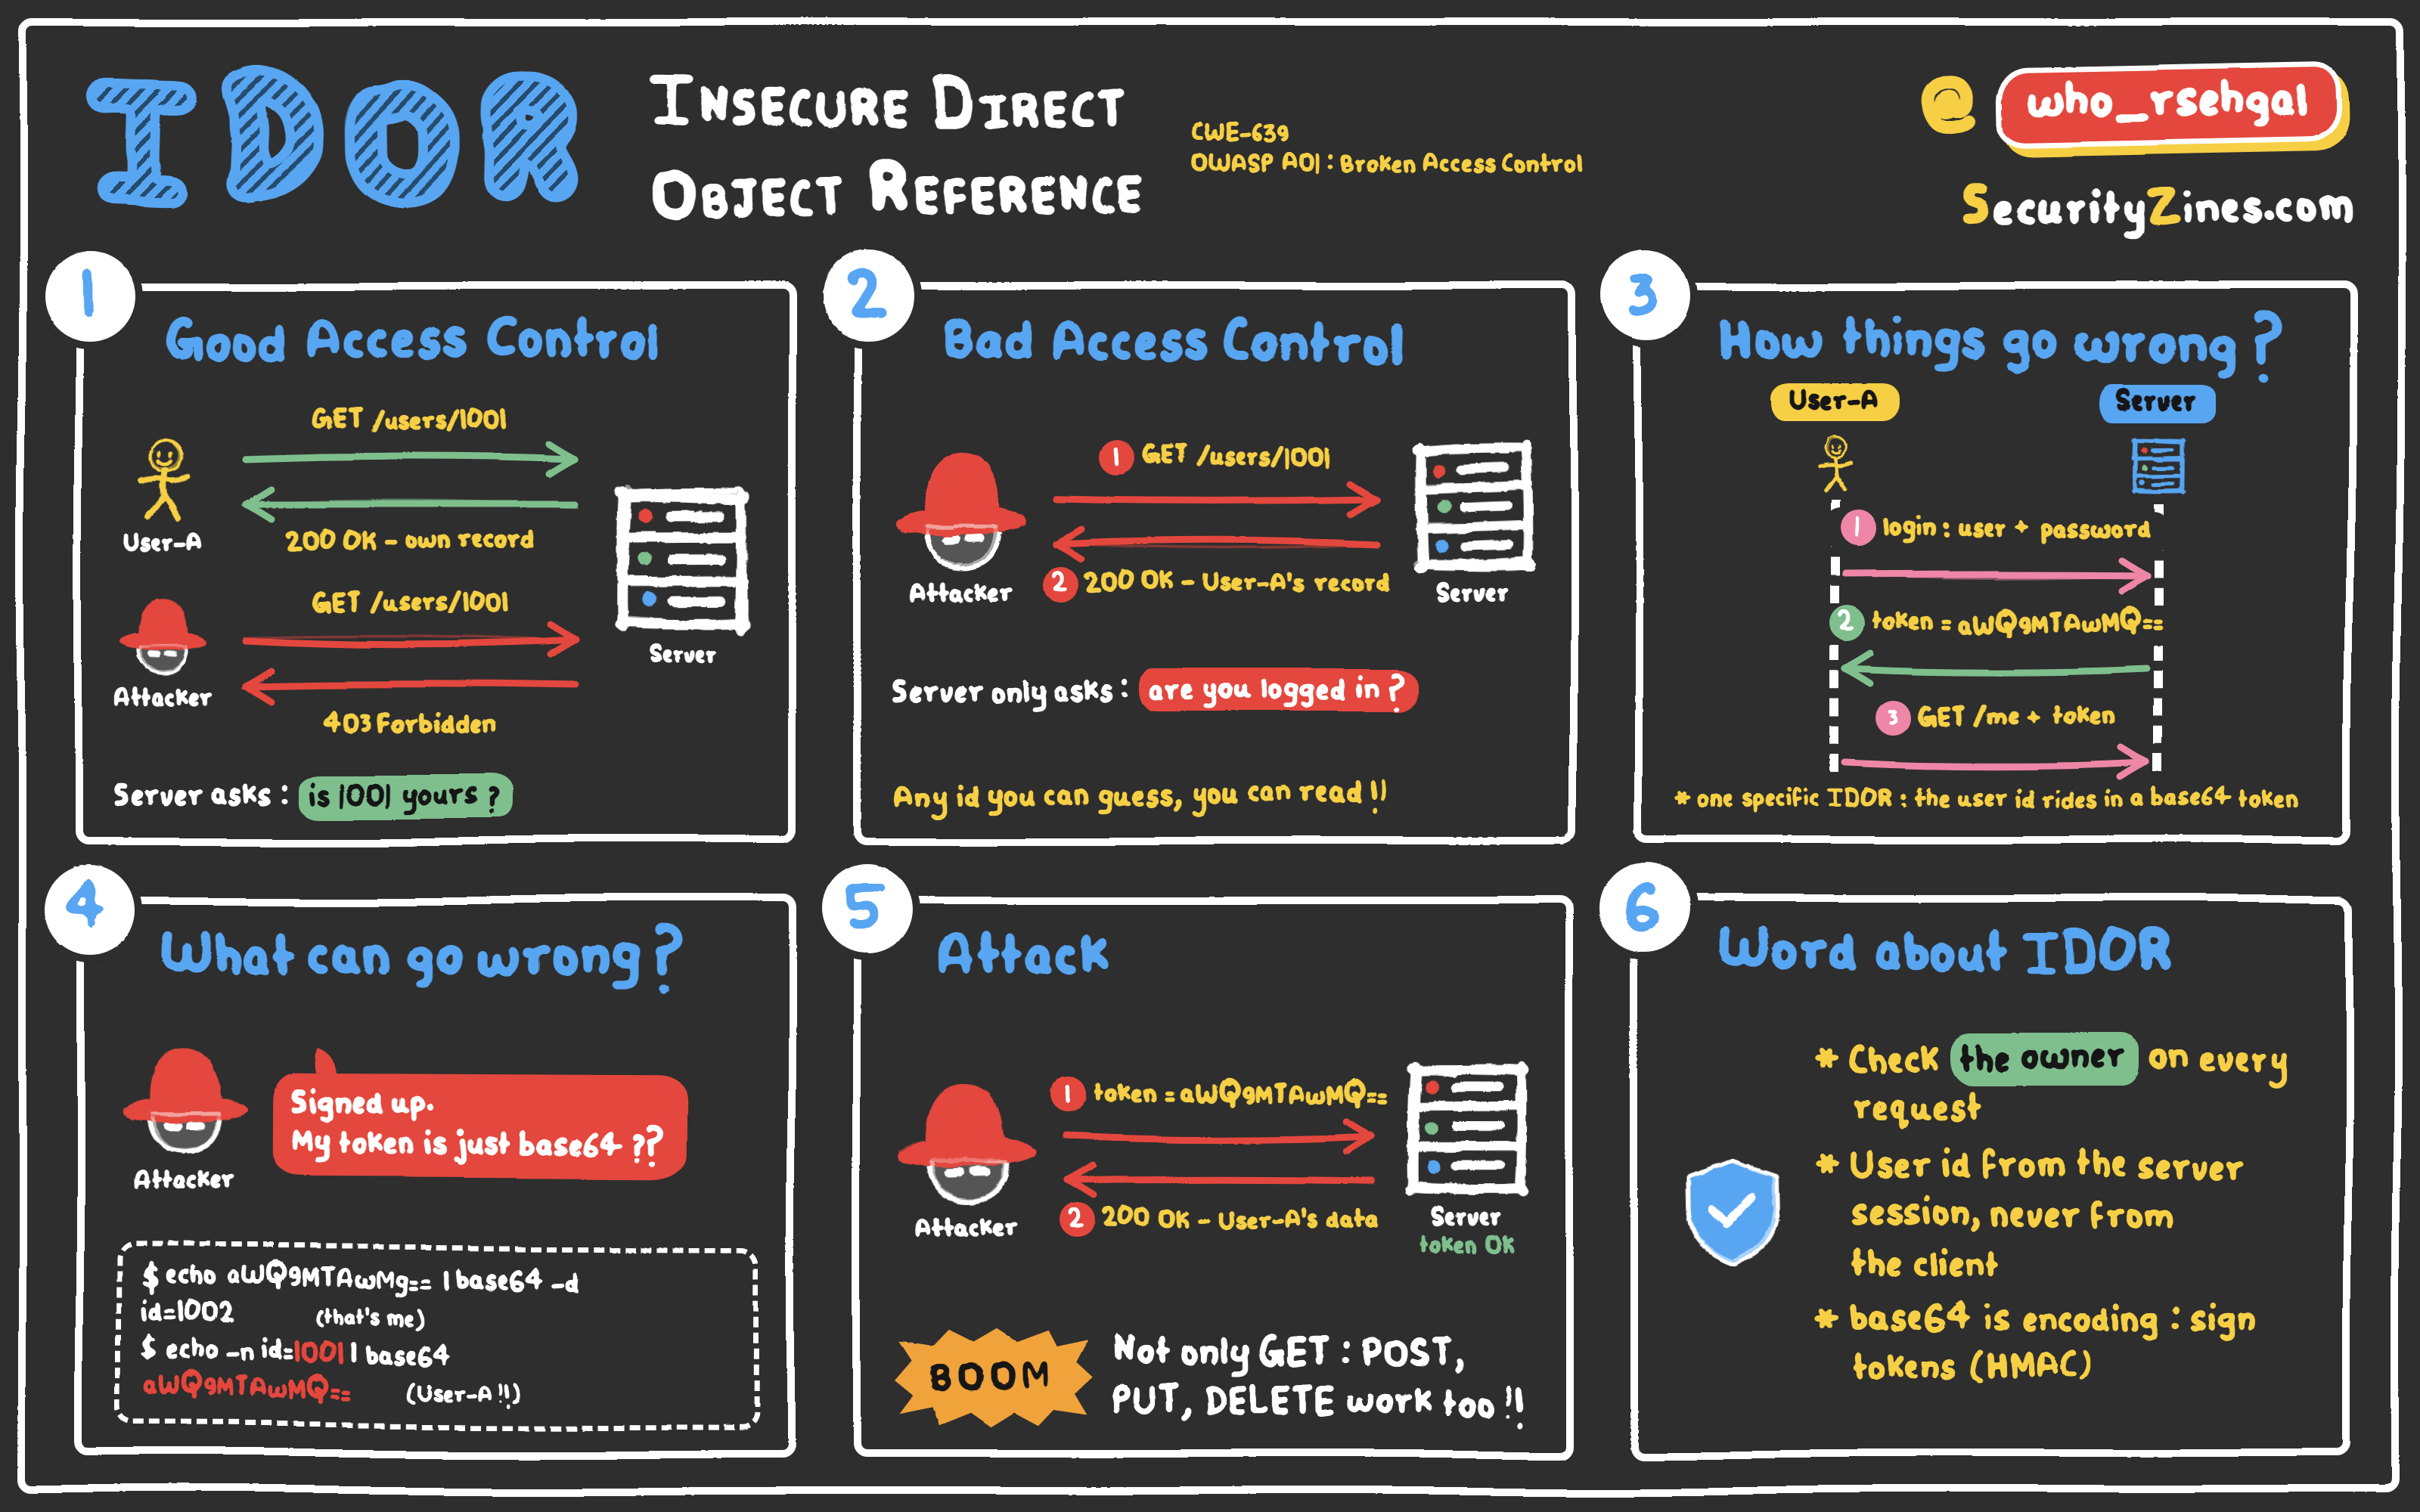
Understanding IDOR (Insecure Direct Object Reference)
What is IDOR? Insecure Direct Object References (IDOR) is a vulnerability that arises when an attacker is able to modify input parameters (e.g., URLs, POST data) to access resources they are not authorized to use. This commonly occurs when user input is not properly validated, allowing attackers to manipulate identifiers (like file paths, user IDs, or document references) to gain unauthorized access.
How It Works: IDOR occurs when an application does not validate or check whether a user has permission to access a specific resource. For example, if a URL contains an ID for a document (`/documents/123`), an attacker could modify the ID to access someone else’s document (`/documents/124`), potentially exposing sensitive information or modifying data.
Why It Matters: IDOR vulnerabilities can lead to unauthorized data access, privacy violations, and even data manipulation. This type of attack can bypass access controls and affect both the security of the application and the integrity of sensitive user data.
Common Use Cases: IDOR is commonly found in web applications that use URL parameters or session IDs to refer to resources. If the application does not properly check user access for each resource, attackers can exploit this weakness to access and manipulate other users' private data or files.
Mitigating IDOR requires careful access control mechanisms and input validation to ensure that users can only interact with their own resources, thus safeguarding user privacy and application integrity.