SecurityZines.com

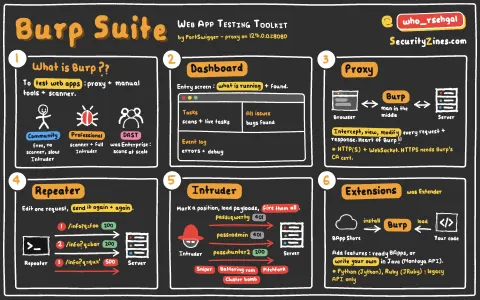
Important tabs of Burp Suite for Web Application Security
Proxy: Burp Suite’s Proxy module is your gateway to intercepting and analyzing HTTP/S traffic between your browser and the server. It allows you to inspect, modify, and debug requests in real-time, making it a powerful tool for understanding how your application communicates and identifying potential vulnerabilities.
Repeater: Need to fine-tune your testing? The Repeater tool lets you send and tweak individual HTTP requests repeatedly. With its intuitive interface, you can test server responses to various inputs, making it ideal for parameter testing and investigating server behavior.
Intruder: Take your testing to the next level with Burp Suite's Intruder. It’s designed for automated testing, enabling you to perform brute-force attacks, fuzzing, or parameter enumeration. Configure payloads and attack patterns to uncover hidden vulnerabilities efficiently.
Extender: Expand Burp Suite’s capabilities with Extender. This module connects you to the Burp App Store, where you can integrate custom extensions or third-party plugins to enhance functionality. Whether you need specialized scanning or automation, Extender adapts Burp Suite to your unique testing needs.
With Burp Suite’s versatile tools, you can uncover, analyze, and address security weaknesses with ease, making it an essential choice for penetration testers and security professionals.
This is the printer-friendly version. See the colour Burp Suite flyer.