SecurityZines.com
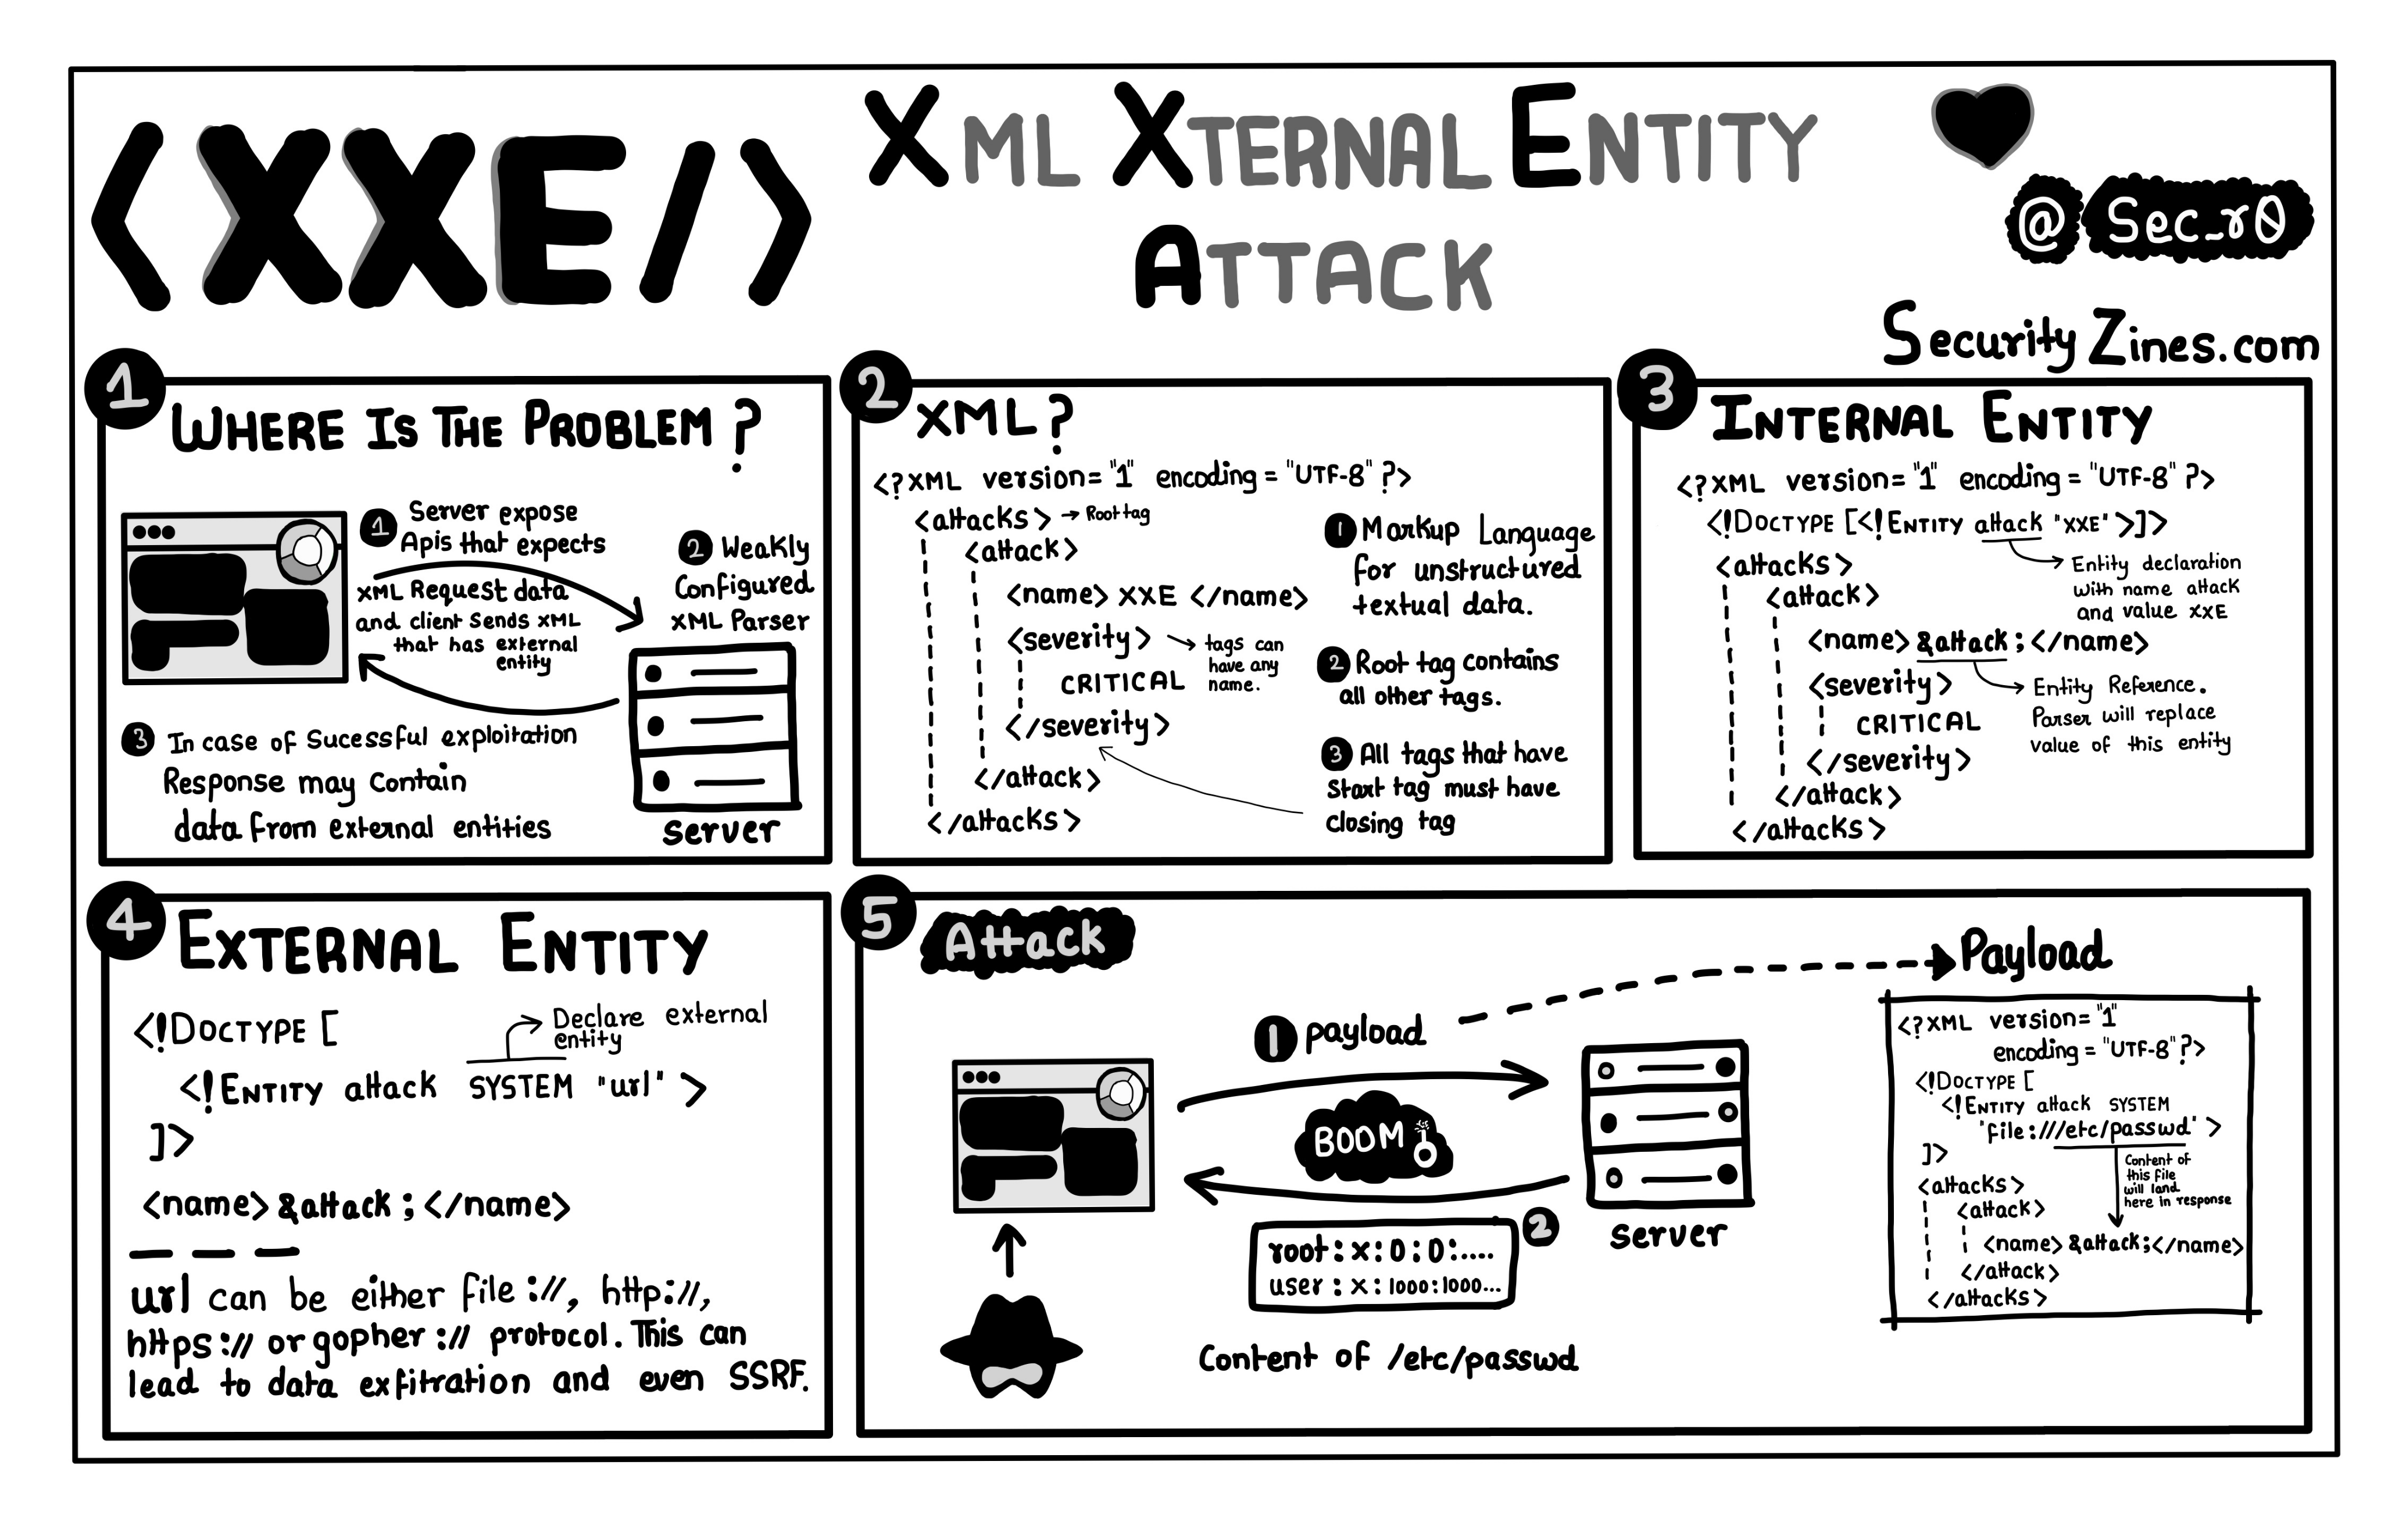
Understanding XML External Entity (XXE)
What is XXE? XML External Entity (XXE) is a type of attack against an application that parses XML input. It occurs when an XML parser processes data that includes a reference to an external entity, allowing an attacker to manipulate the data and interact with the server.
How XXE Works: An attacker injects malicious XML content into an application, which is then parsed by the XML processor. By defining an external entity, the attacker can read local files, perform port scans, or execute arbitrary code on the server.
Types of XXE Attacks: - Internal Entity: Refers to entities defined within the XML document. - External Entity: Refers to entities defined outside the XML document, such as files or URLs. - Parameter Entity: Refers to entities defined in the DTD (Document Type Definition) section of the XML document.
Why XXE Matters: XXE attacks can have serious consequences, including: - Data Theft: Access to sensitive information stored on the server. - Server-Side Request Forgery (SSRF): Making requests to internal systems or performing port scans. - Denial of Service (DoS): Overloading the server by reading large files or performing resource-intensive operations.
Preventing XXE: To mitigate XXE vulnerabilities, consider the following best practices: - Disable External Entities: Configure the XML parser to disallow external entities. - Use Whitelists: Define a list of allowed entities to restrict access to specific resources. - Sanitize Input: Validate and sanitize XML input to prevent malicious content. - Update Libraries: Keep XML parsers and libraries up to date to patch known vulnerabilities.
This is the printer-friendly version. See the colour XXE flyer.