SecurityZines.com
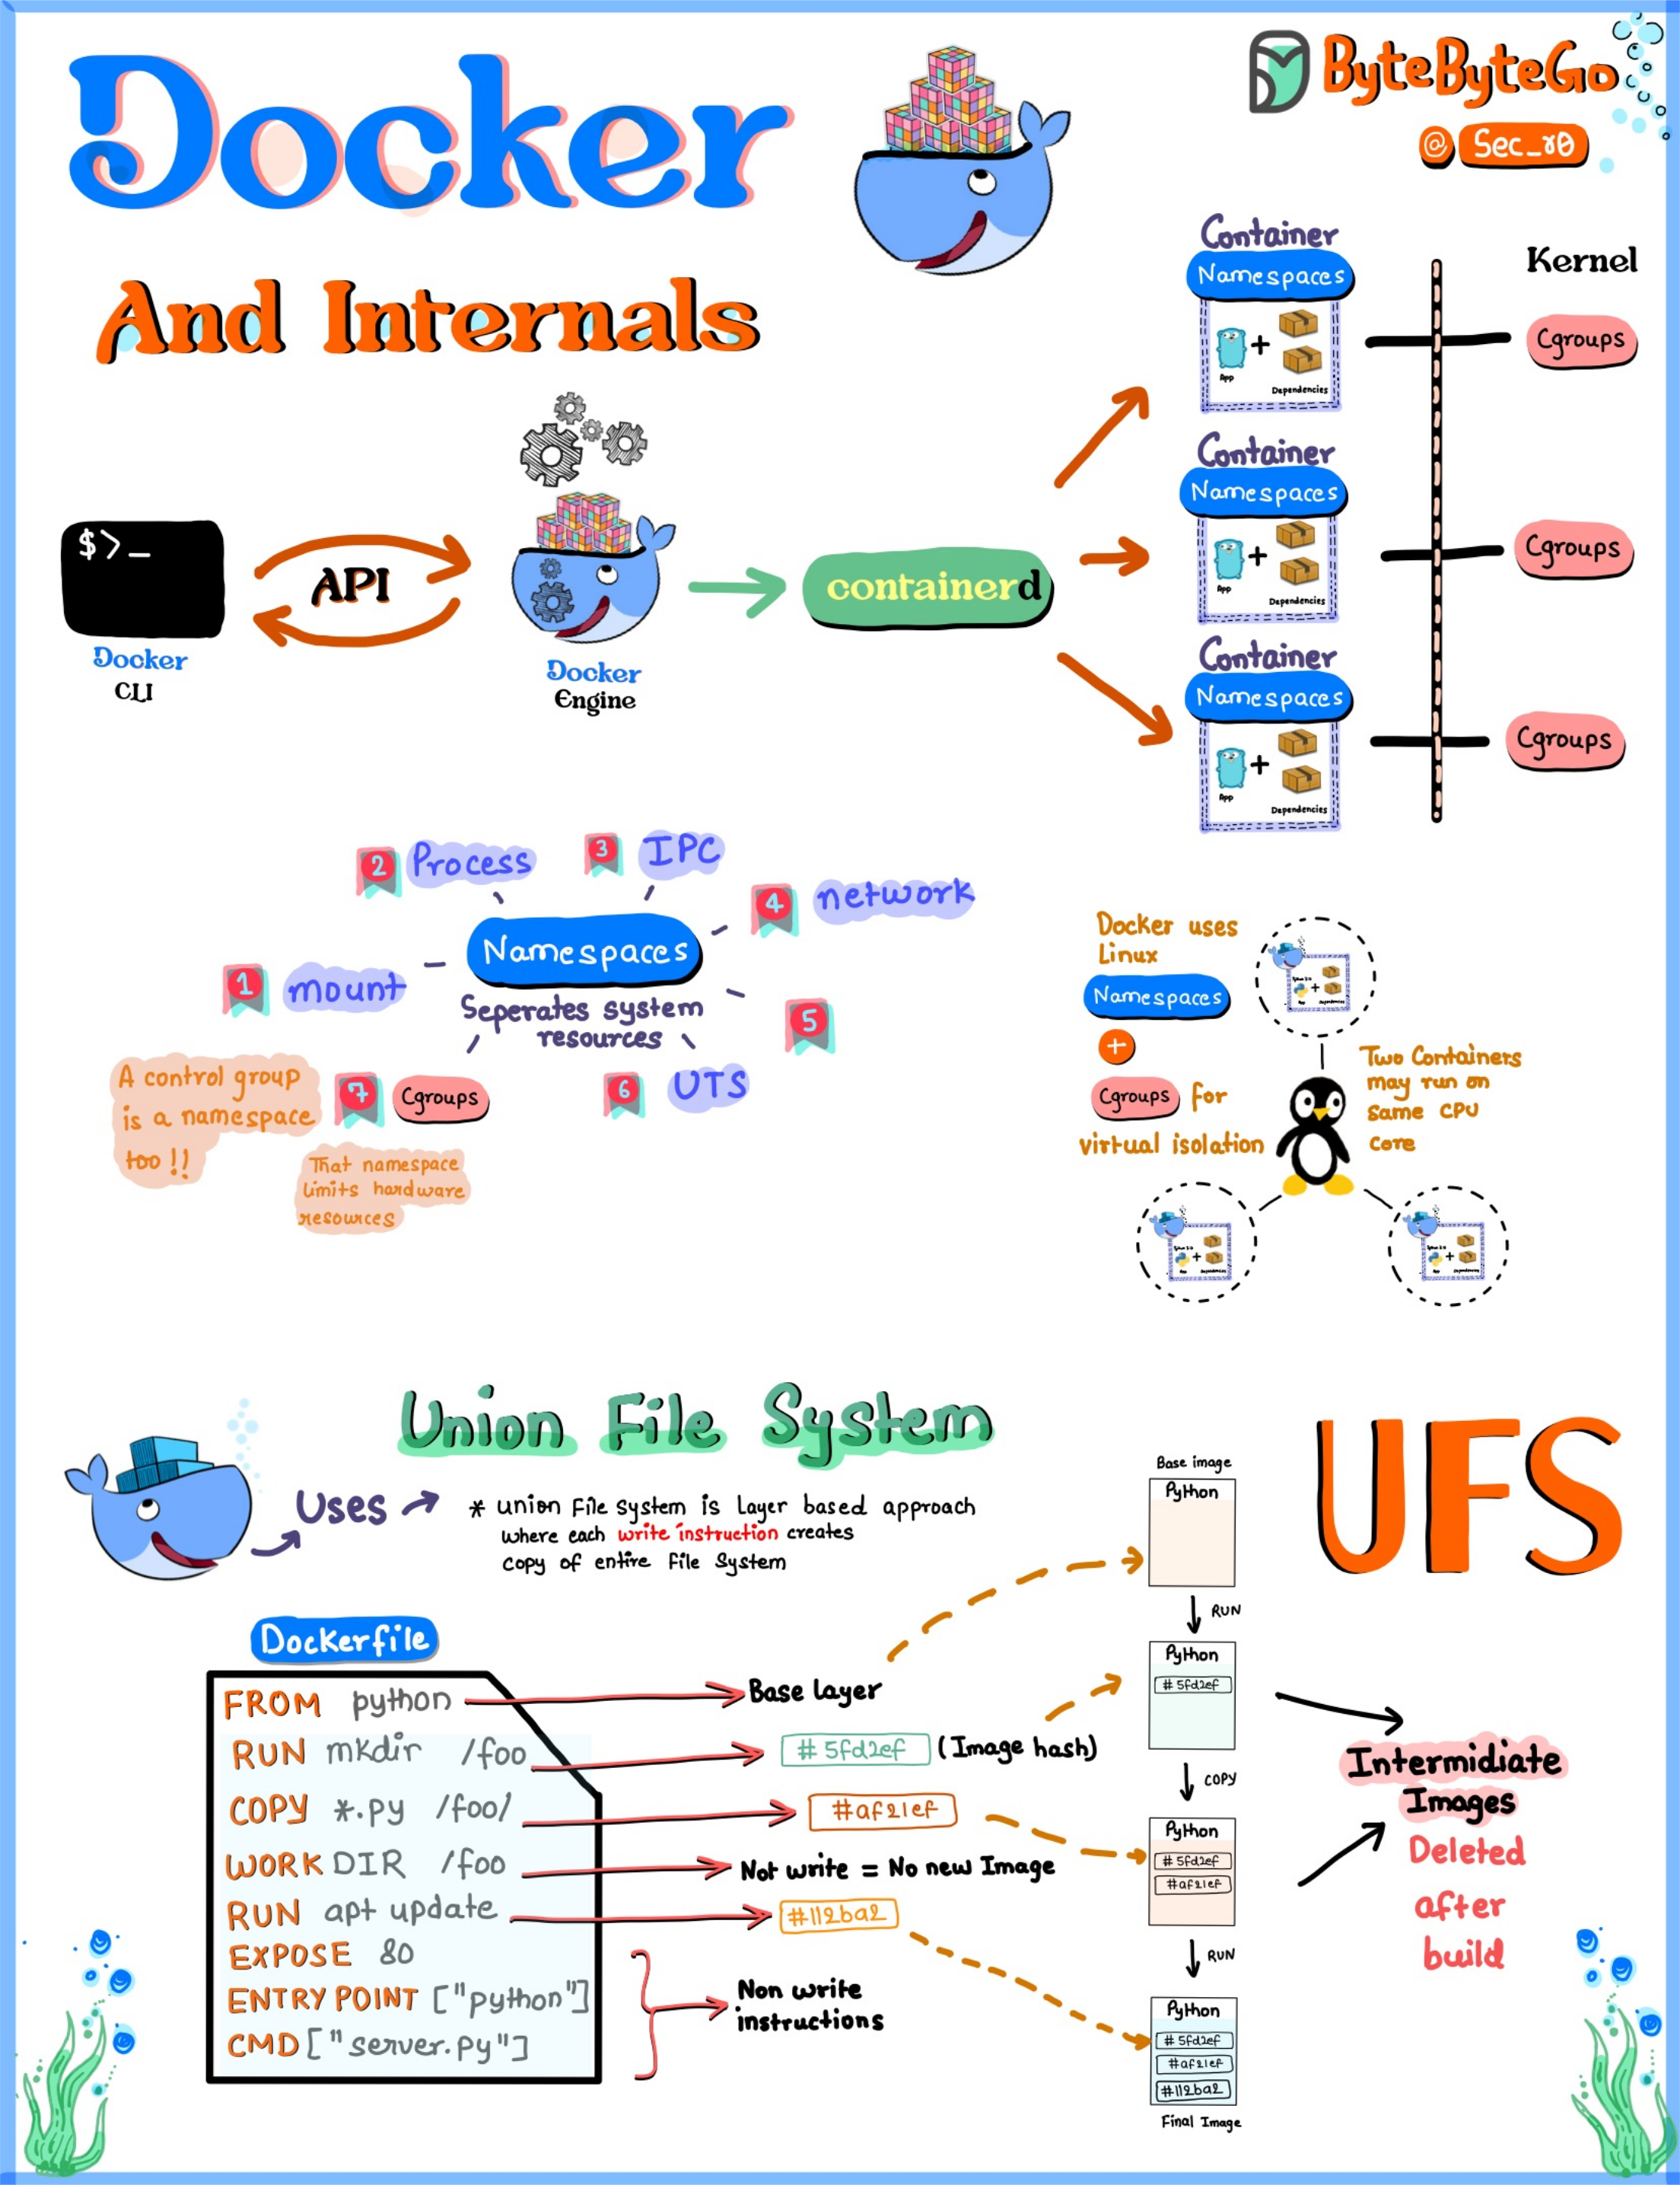
What a container is: not a small VM, but a normal Linux process with a restricted view. Namespaces isolate what it can see (PIDs, network, mounts, users) and cgroups limit what it can use (CPU, memory).
Images: read-only layers stacked by a union filesystem (overlayfs), with a thin writable layer on top for each container. That is why images share layers and start fast.
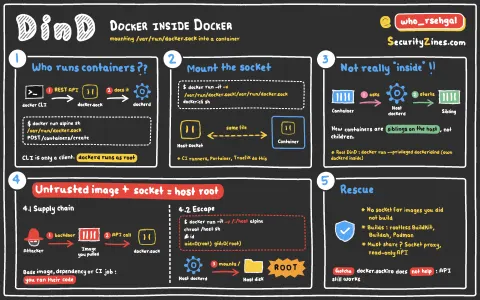
Why it matters: all containers share the host kernel. Running as root, --privileged, or a mounted Docker socket can turn a container compromise into a host compromise.