SecurityZines.com
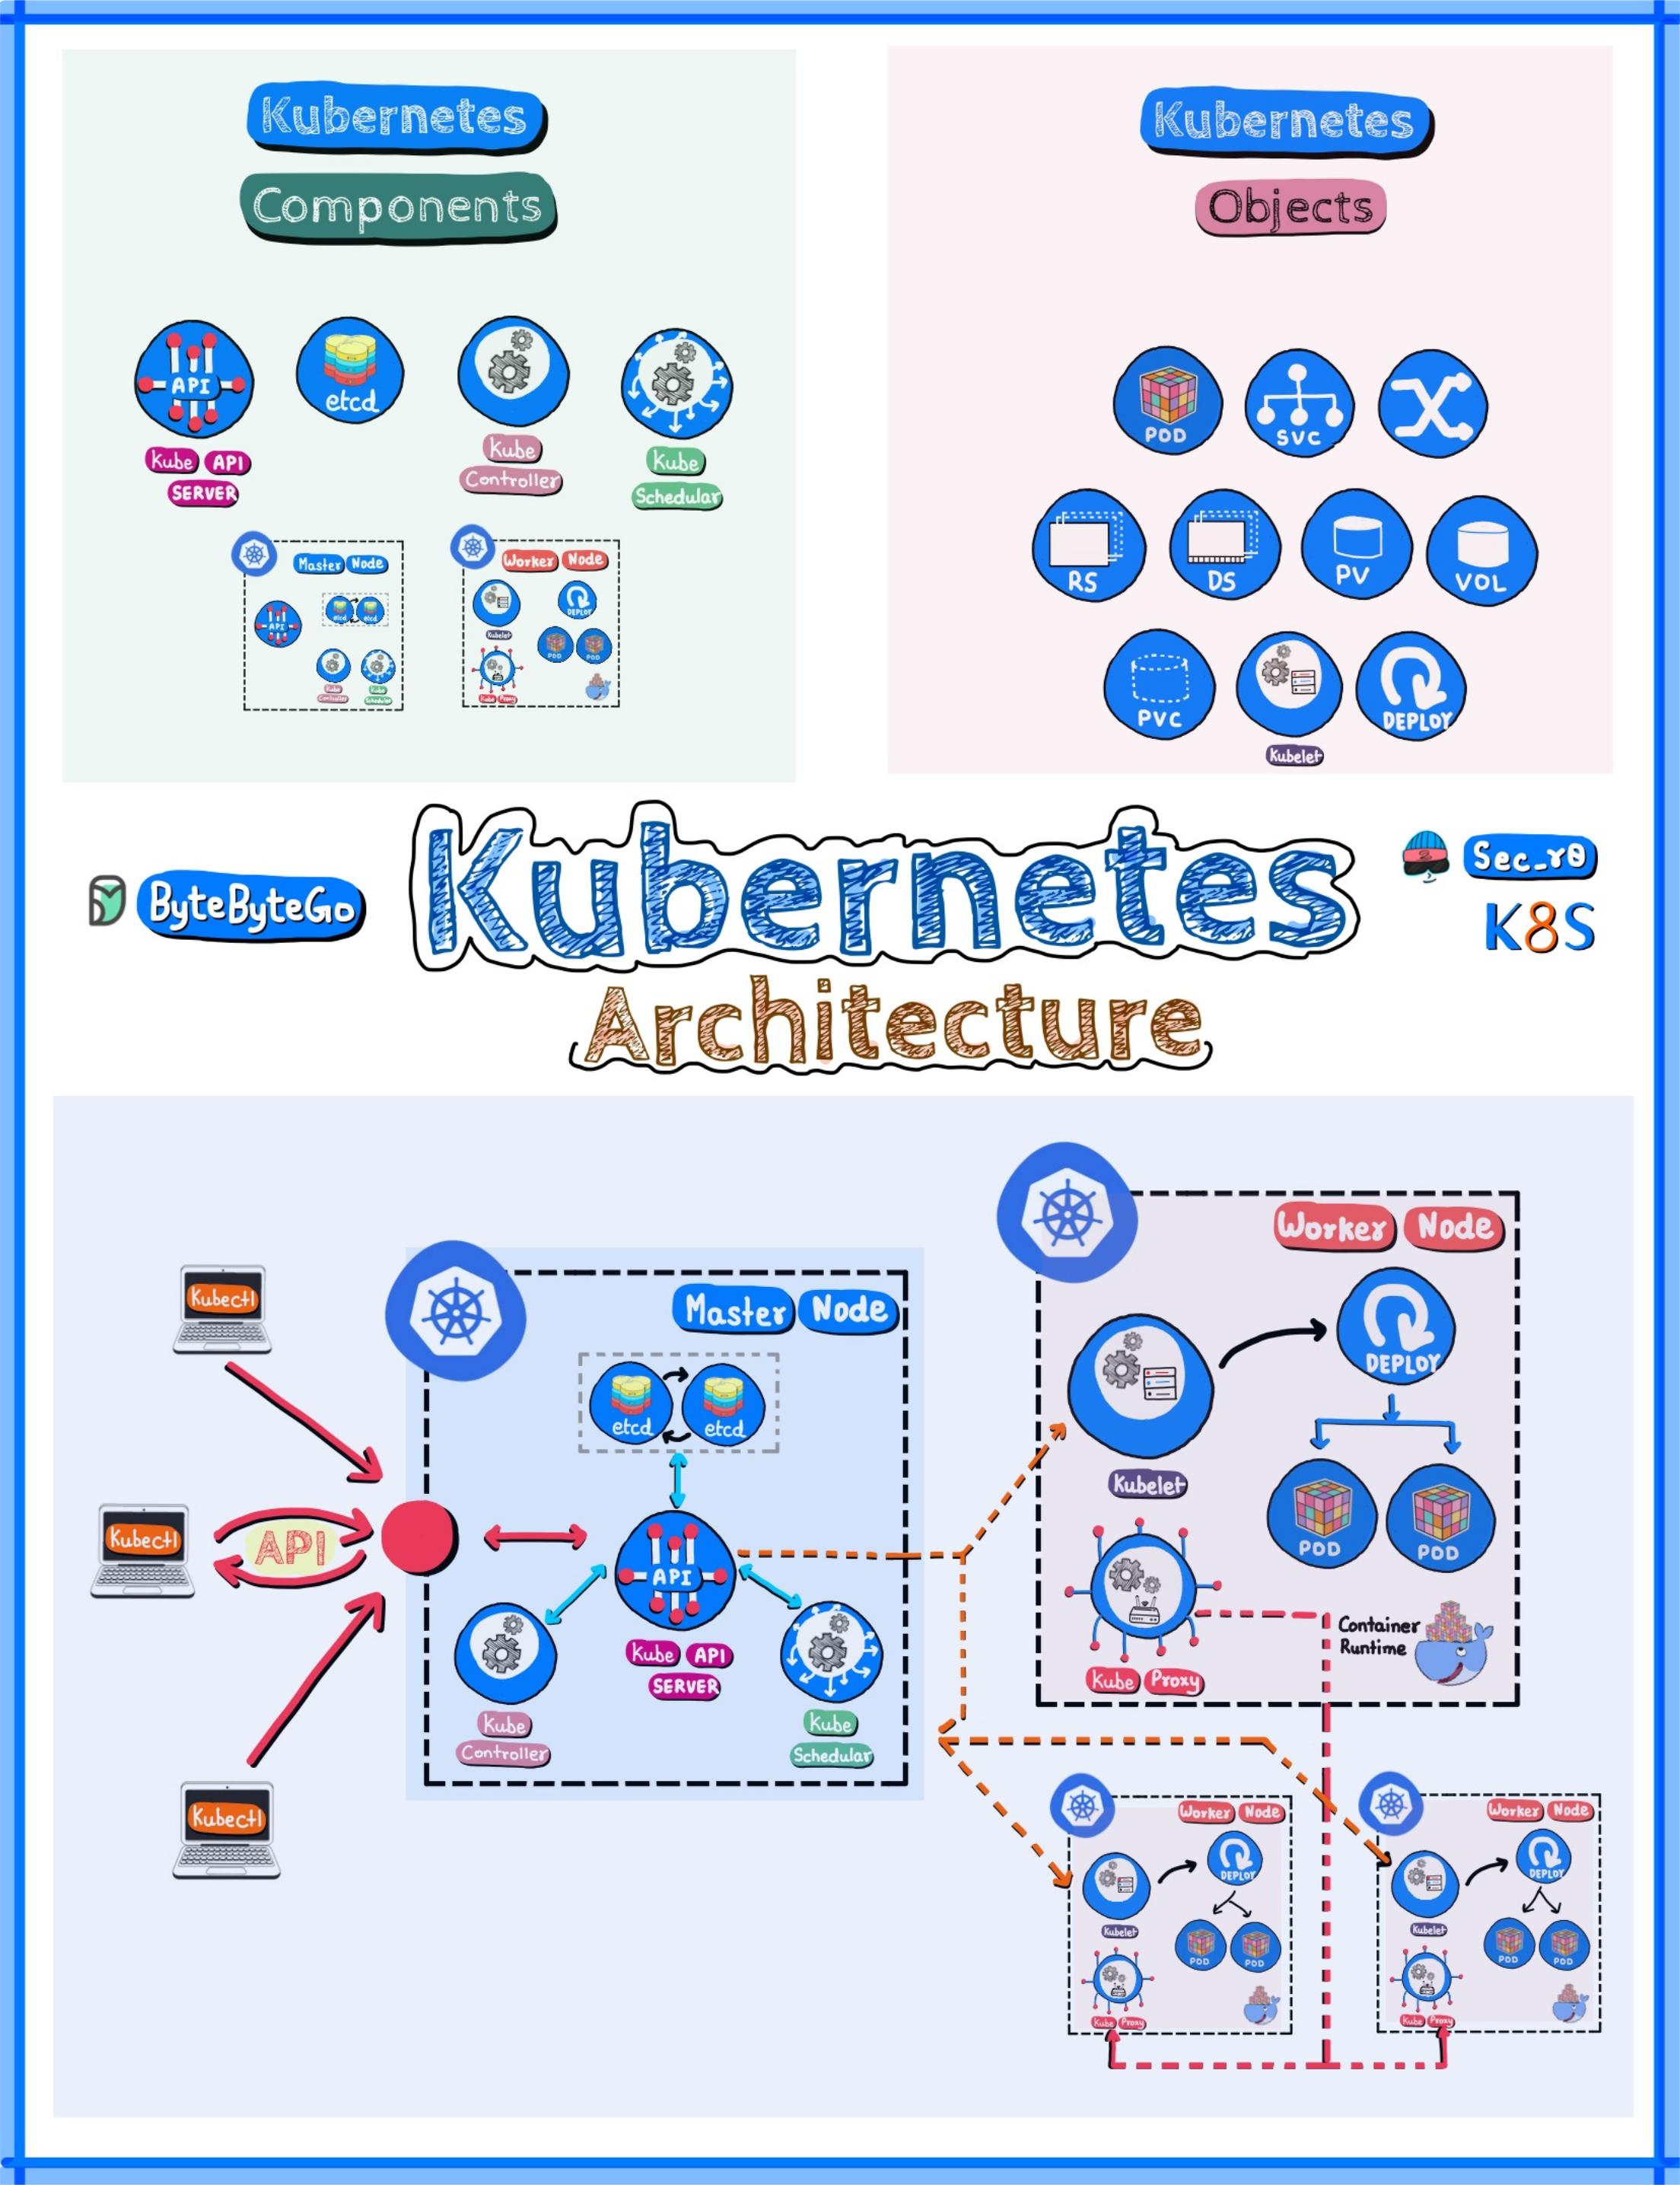
Control plane: the API server (front door for everything), etcd (the cluster's key-value store of truth), the scheduler (places pods on nodes) and the controller manager (loops that drive actual state toward desired state).
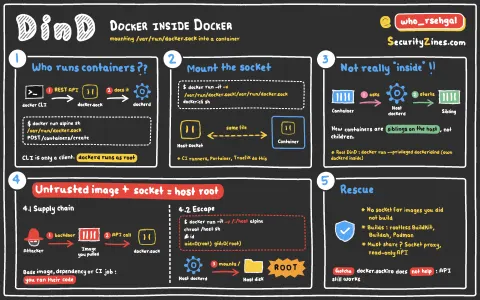
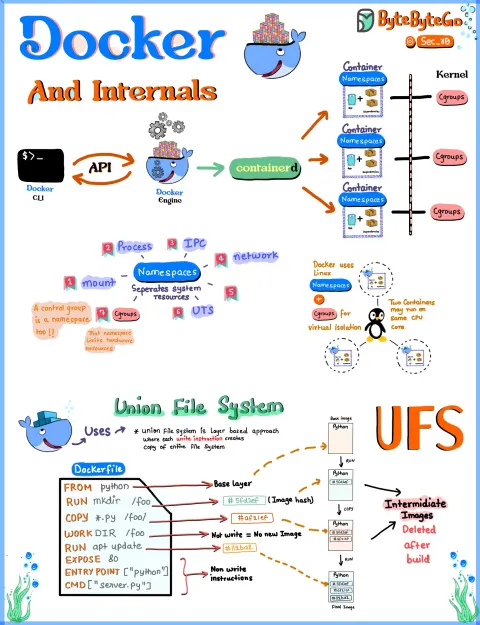
Worker nodes: the kubelet runs pods, a container runtime such as containerd runs containers, and kube-proxy handles service networking.
Why it matters: whoever controls the API server or etcd controls the cluster. Keep them private, require TLS and authentication, and audit access.