SecurityZines.com
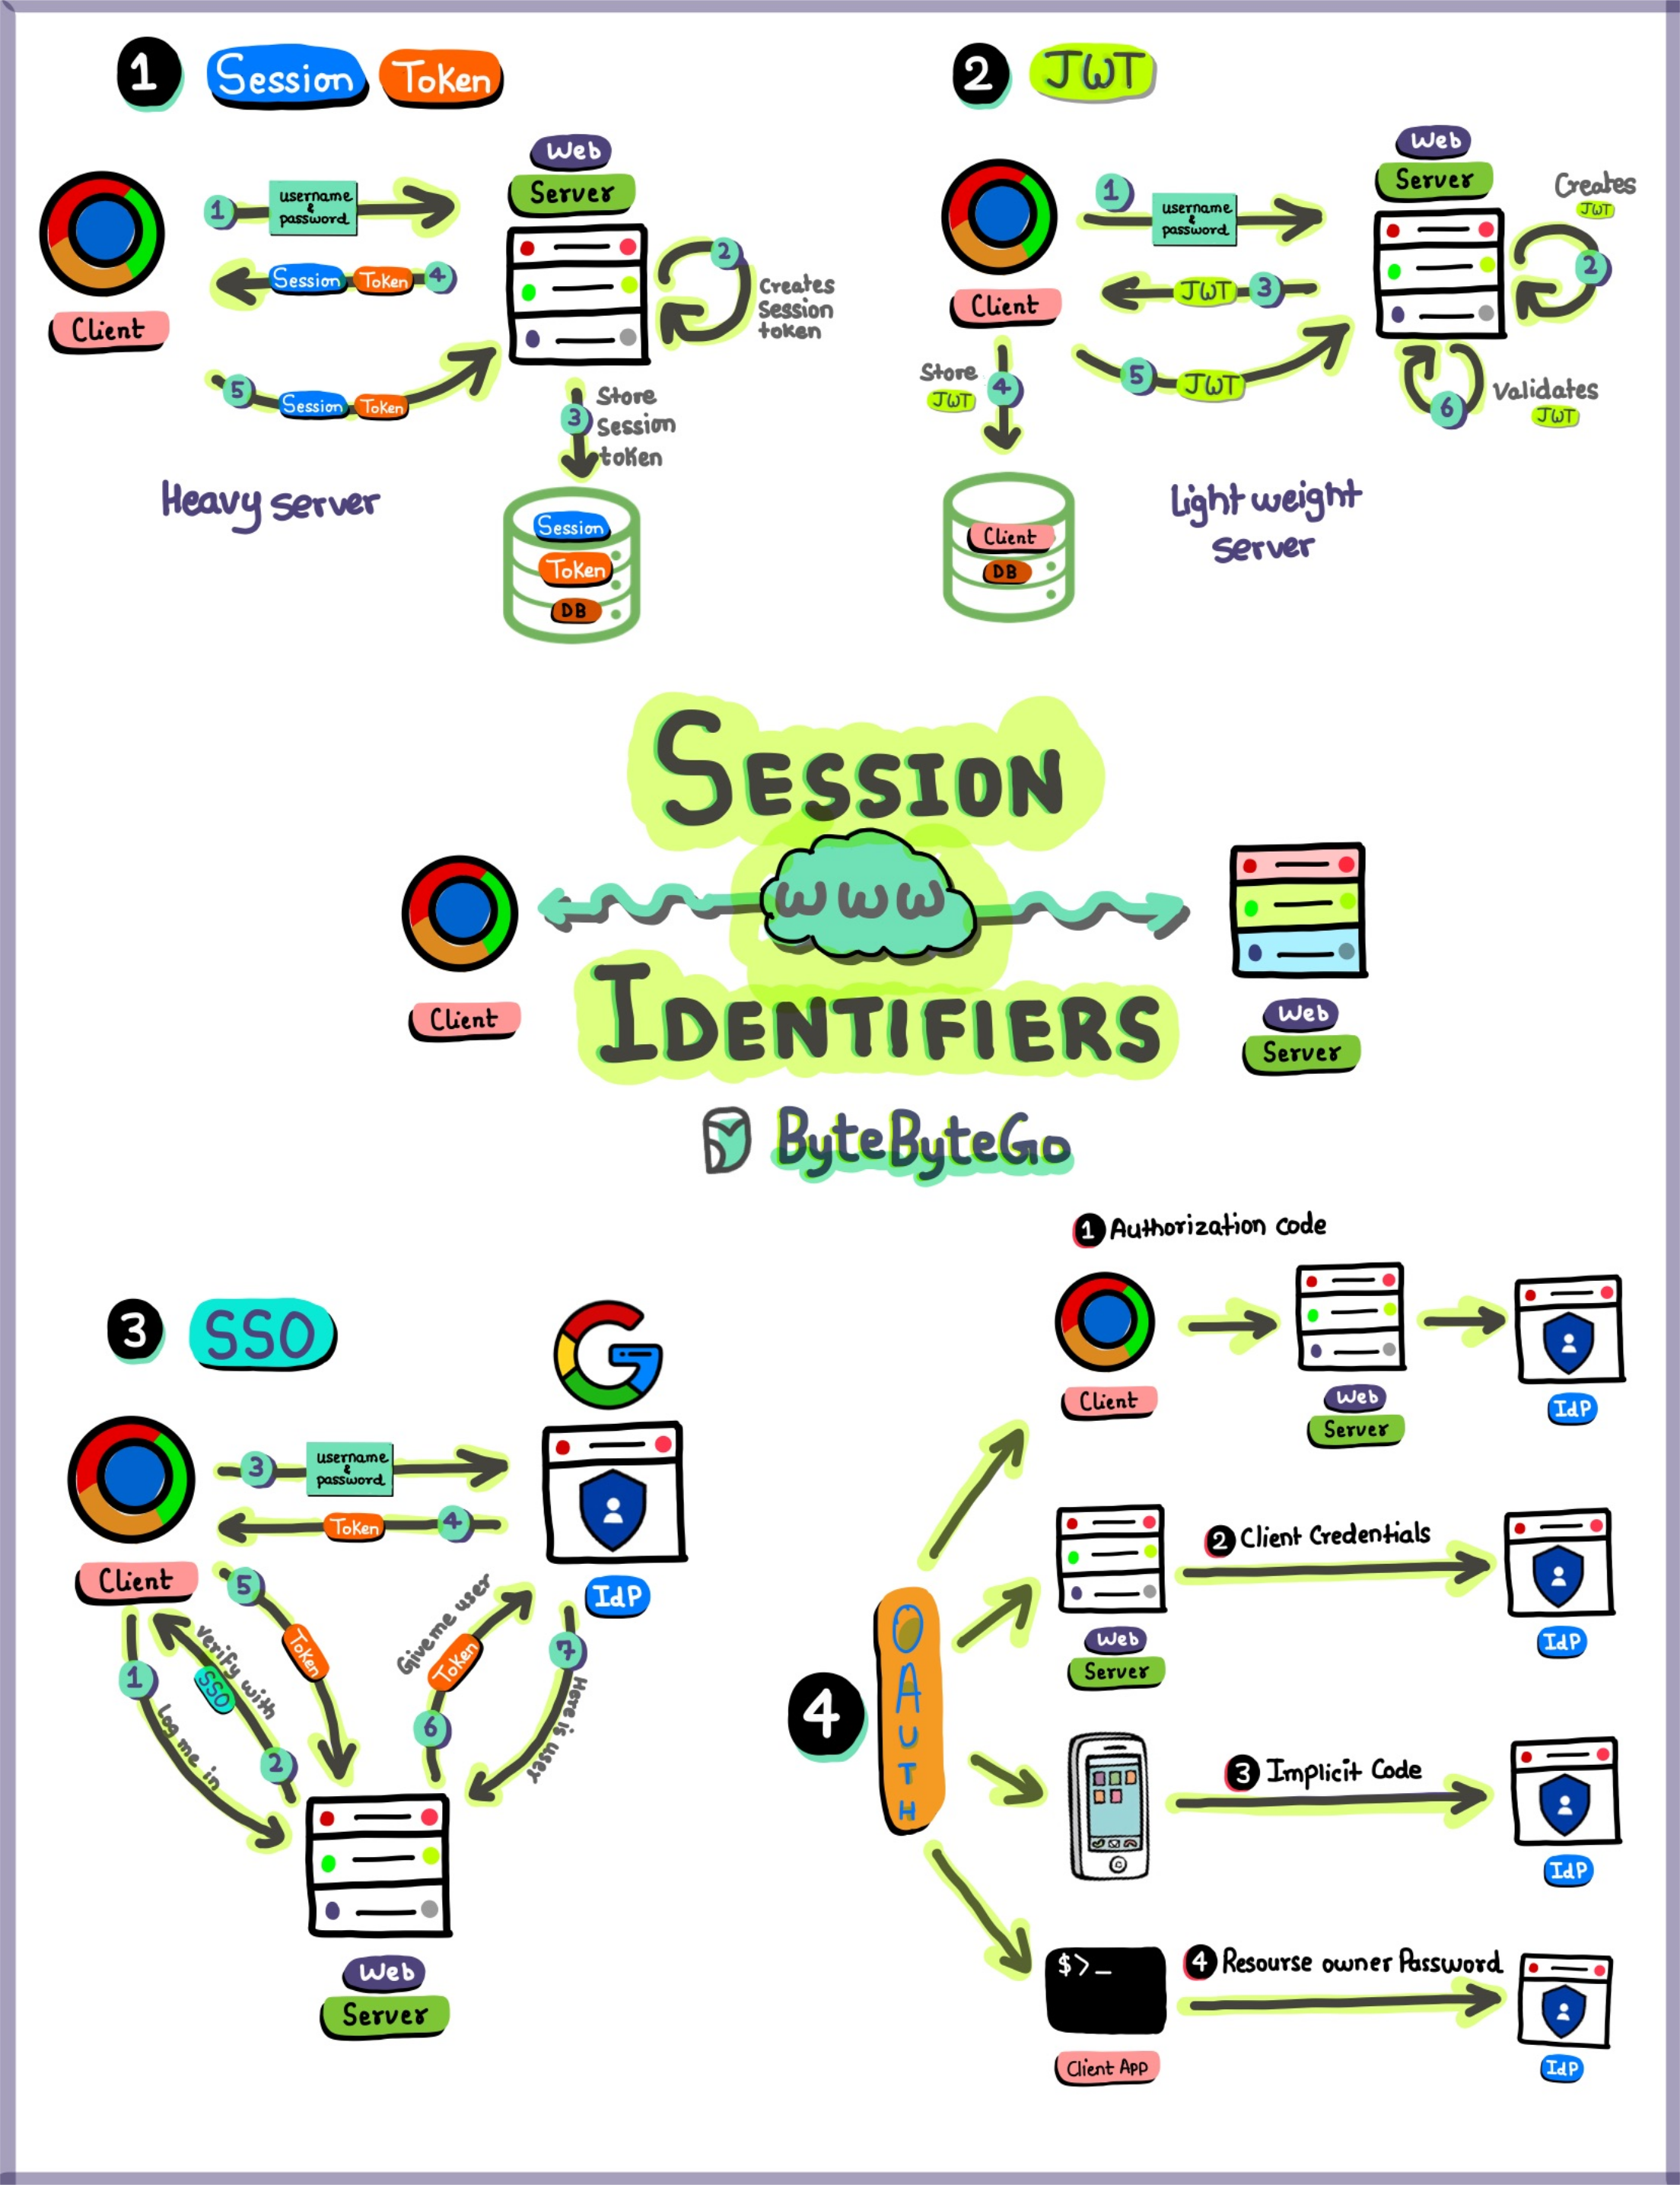
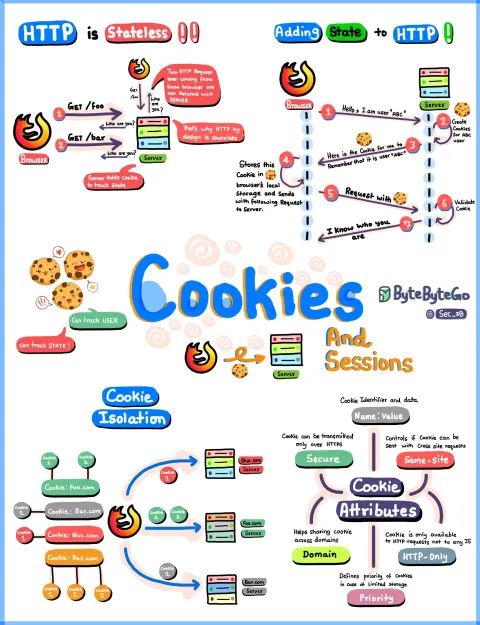
What it is: a session identifier is the random value that ties a browser to its server-side session, usually sent in a cookie.
What makes it safe: enough randomness that it cannot be guessed (at least 128 bits from a cryptographic generator), no meaning inside it, a new ID issued at login (stops session fixation), and expiry on idle and on logout.
Common mistakes: IDs in URLs (they leak through logs and the Referer header), sequential or time-based IDs, and cookies without HttpOnly, Secure and SameSite.