SecurityZines.com
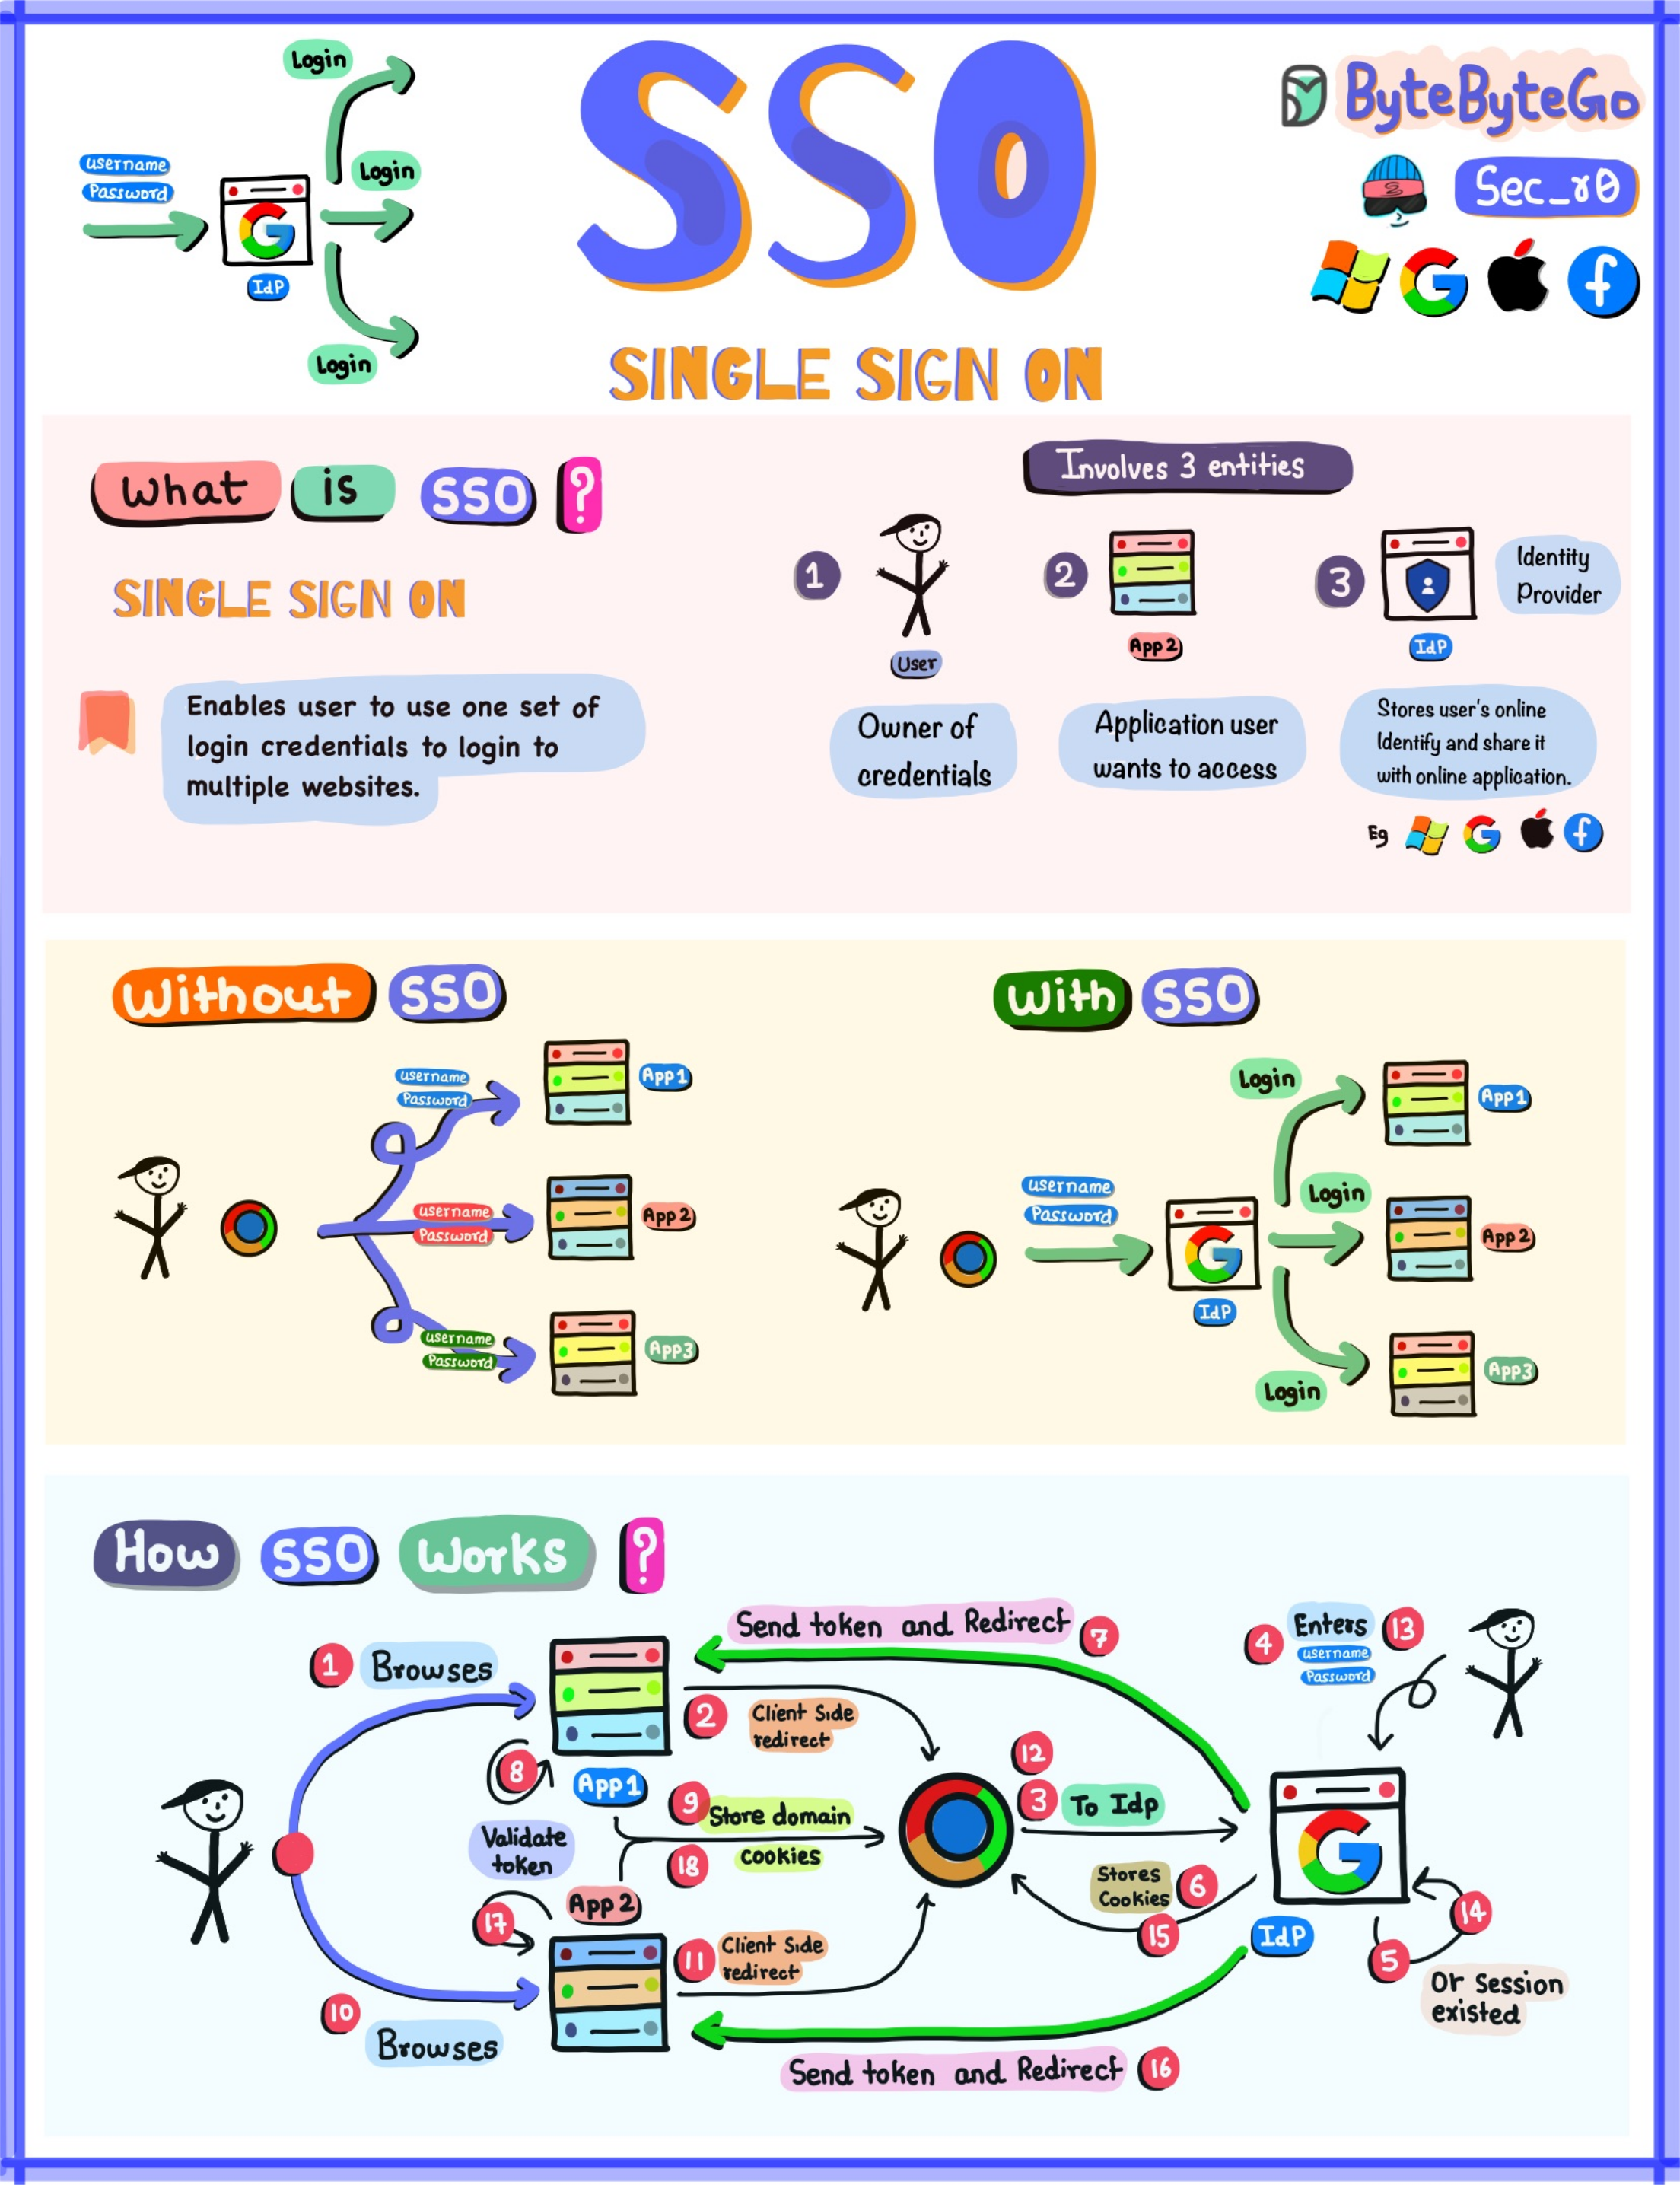
What it is: with SSO you authenticate once at an identity provider (IdP) and every connected app (service provider) trusts that login instead of keeping its own passwords.
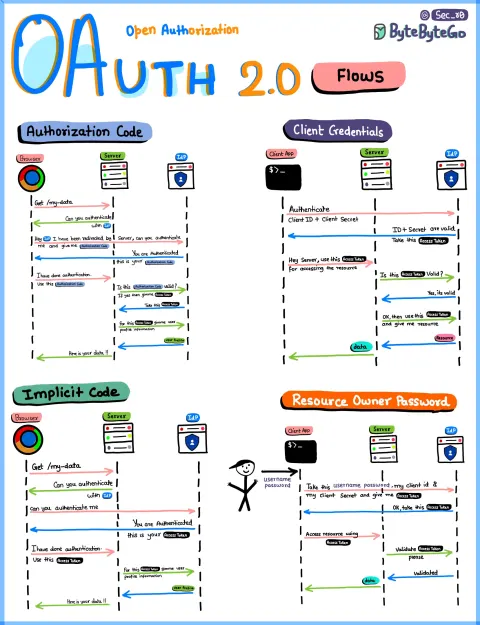
How it works: an app redirects you to the IdP; after login the IdP sends back a signed assertion (SAML) or ID token (OpenID Connect) that the app verifies and turns into a local session.
Why it matters: fewer passwords, central MFA and instant off-boarding. The flip side: the IdP becomes a single point of failure, so signature validation, audience checks and session timeouts on every app really count.