SecurityZines.com
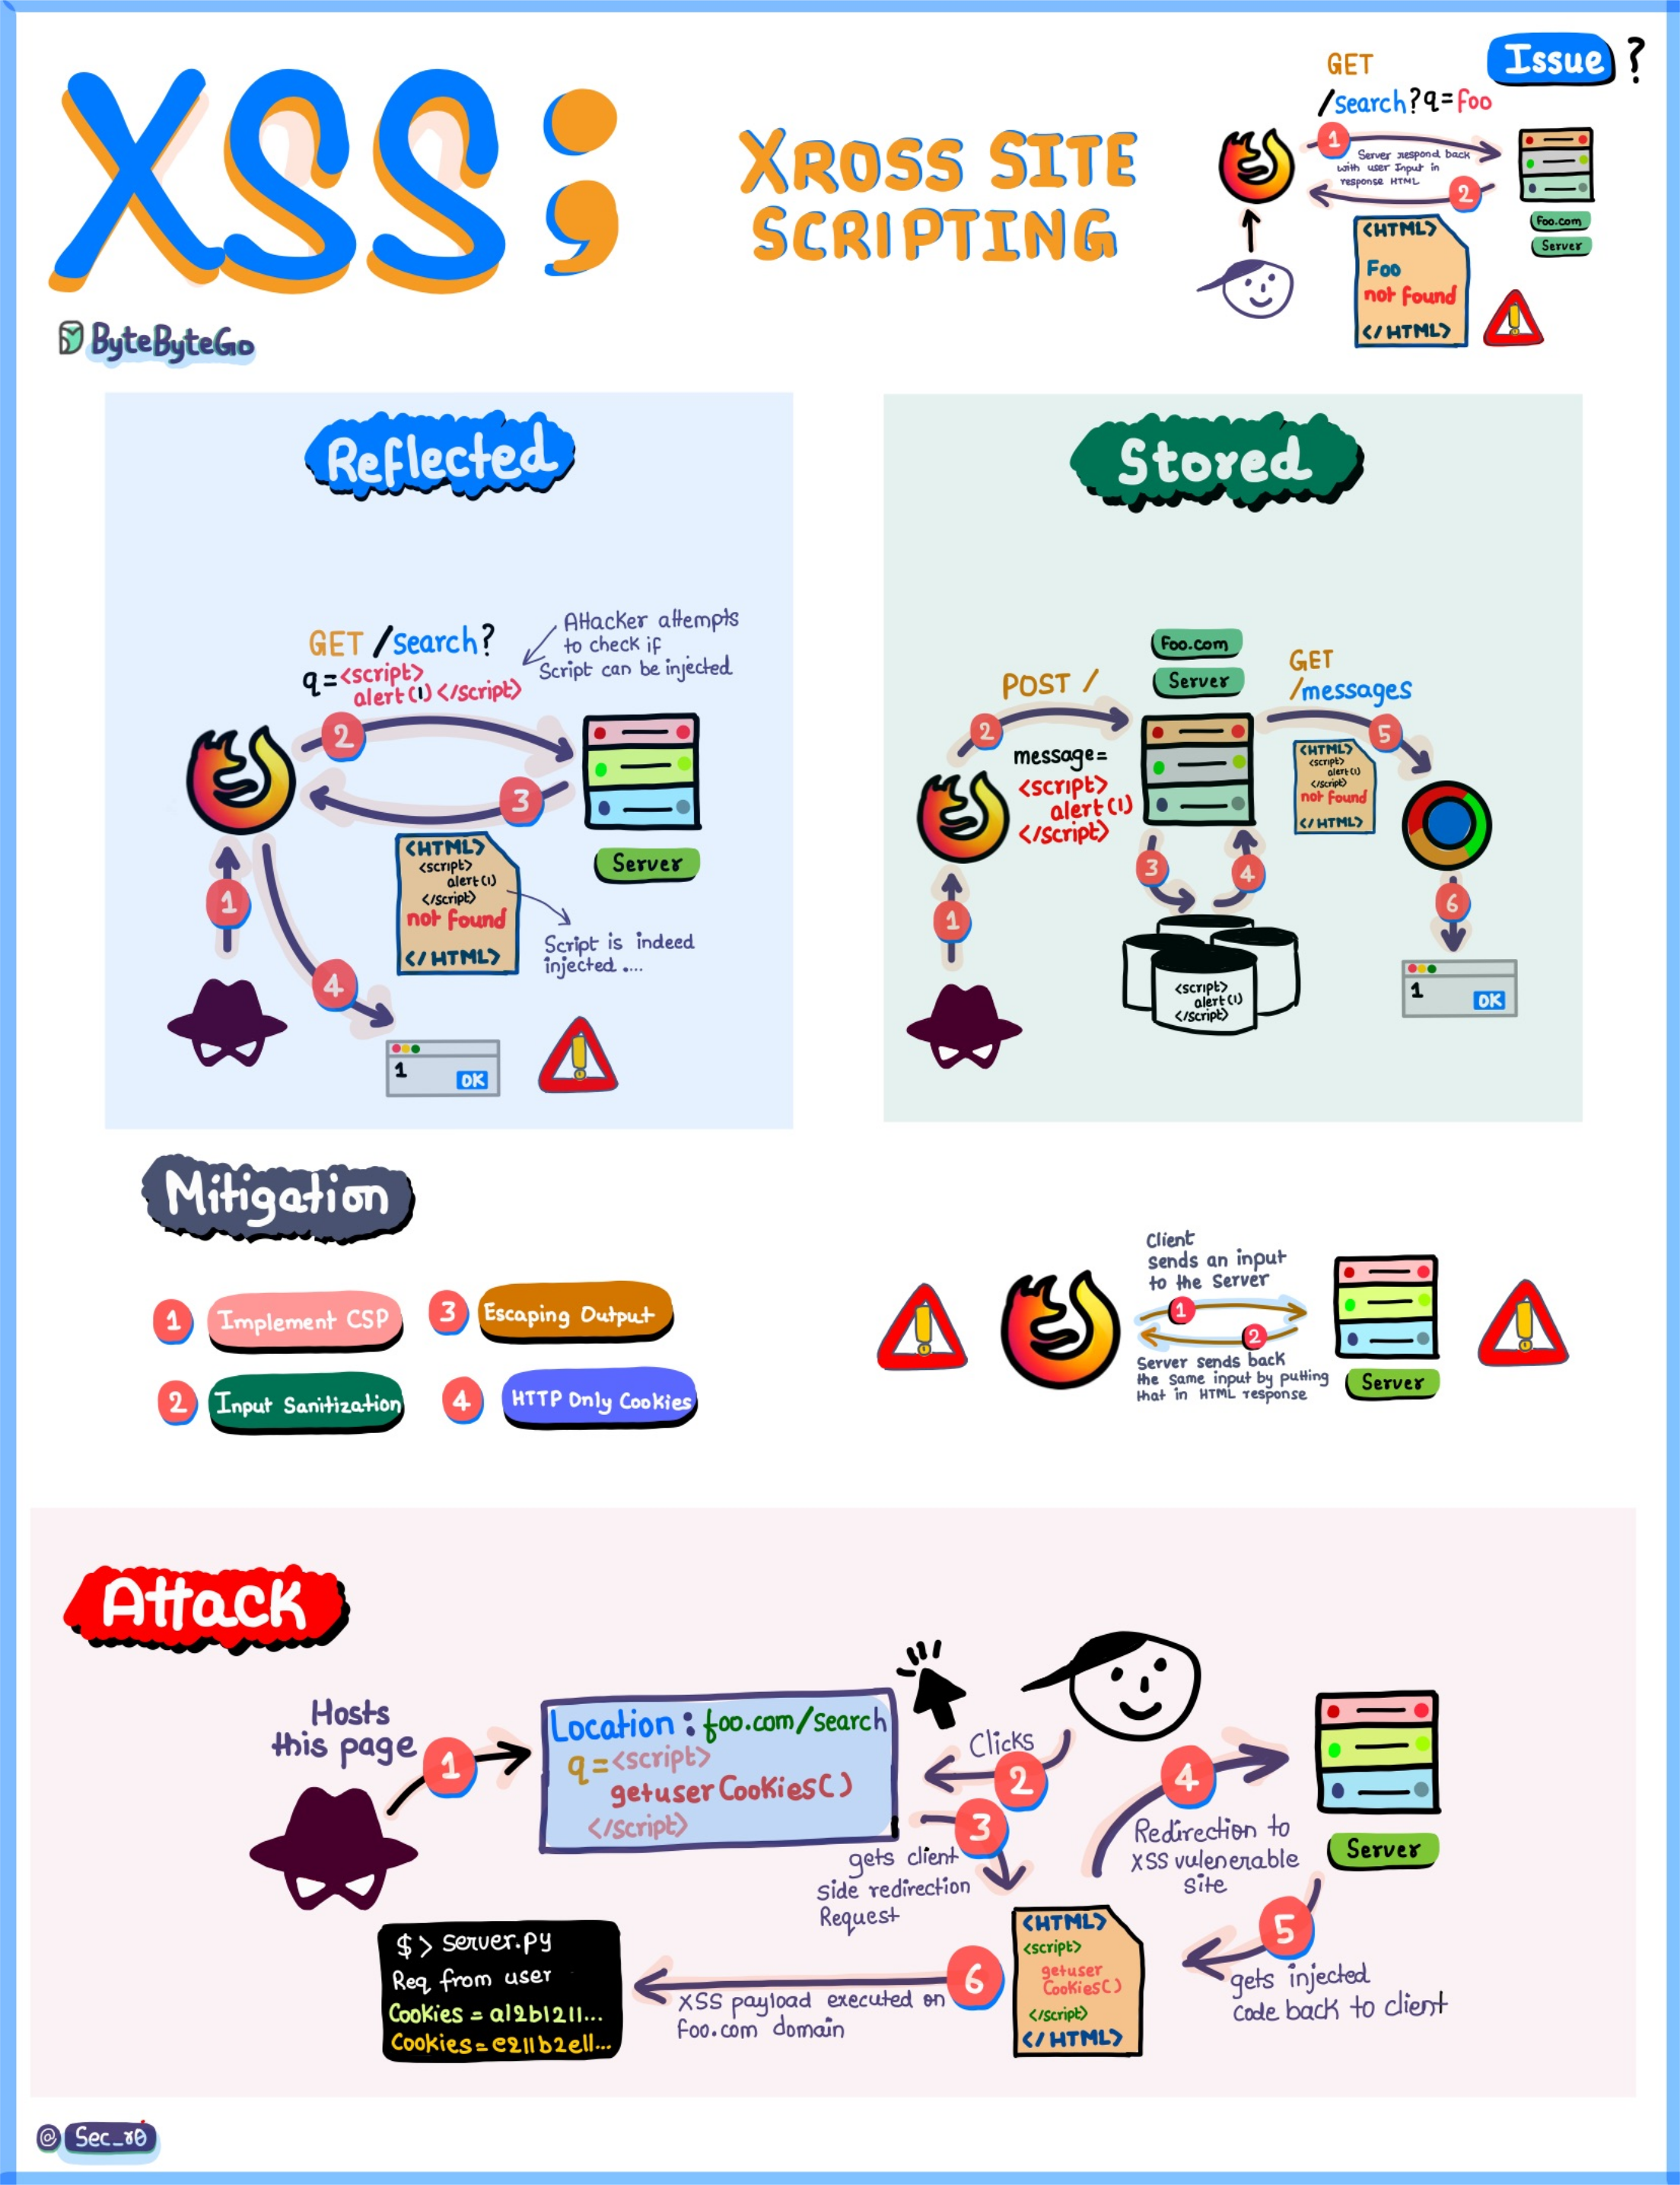
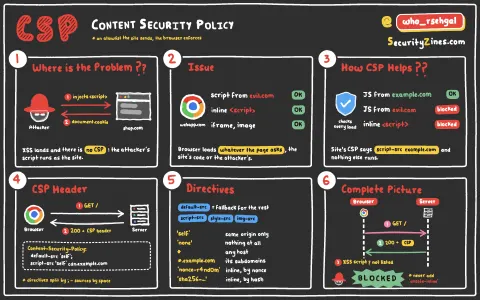
What it is: XSS happens when an app puts untrusted input into a page without encoding it, so the browser runs the attacker's script with the site's privileges.
Three kinds: reflected (the payload bounces off a request, often a link), stored (saved in the database and served to every visitor) and DOM-based (client-side JavaScript writes input into the page).
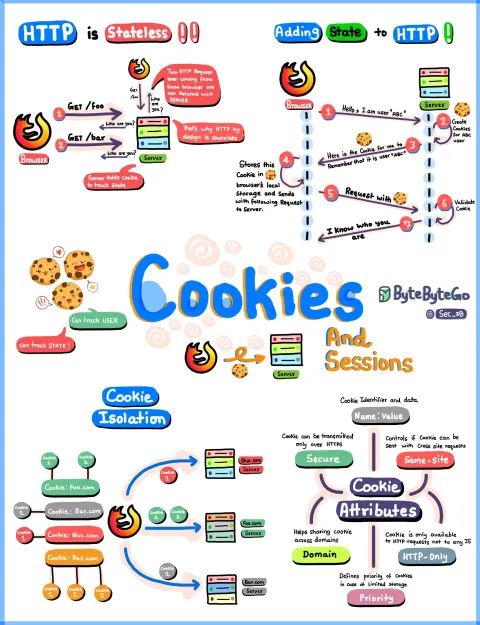
Defences: context-aware output encoding, frameworks that escape by default, avoiding innerHTML with user data, a strict Content Security Policy, and HttpOnly cookies to limit what a script can steal.